SafeLine
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
- 23k
- Go
- GPL-3.0
- 9 d ago
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
Mobile Security Framework (MobSF) is an automated, all-in-one mobile application (Android/iOS/Windows) pen-testing, malware analysis and security assessment framework capable of performing static and dynamic analysis.
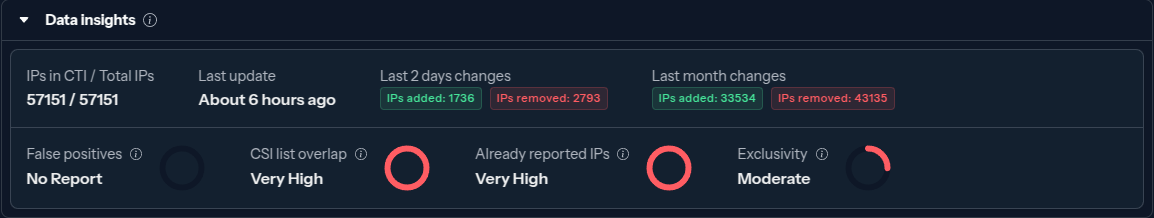
Open-source IDS/IPS, WAF and bot detection for Linux, Windows, Docker and Kubernetes, with a crowdsourced blocklist of malicious IPs.
Source code for Hacker101.com - a free online web and mobile security class.
A list of resources for those interested in getting started in bug bounties
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24 core vulnerability classes, plus enterprise identity + infrastructure attack matrices.
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and Builds. Protect yourself in 30 seconds with the LunaTrace GitHub App: https://github.com/marketplace/lunatrace-by-lunasec/
Stop half-done APIs! Cherrybomb is a CLI tool that helps you avoid undefined user behaviour by auditing your API specifications, validating them and running API security tests.
Modern Python library for HTTP security headers with safe defaults, configurable presets, and first-class ASGI/WSGI middleware (FastAPI, Django, Flask, Shiny, and more).
Reusable prompts for a structured, evidence-first bug bounty hunting workflow
An Axum-based Rust web framework with Lean 4-verifiable application kernels that run on servers, bare-metal embedded devices, and GPUs, plus integrated security testing.
Website specification — HTML, accessibility, security, SEO, agent-readiness. Platform-agnostic, sourced, MIT.
Caddy WAF (Regex Rules, IP and DNS filtering, Rate Limiting, GeoIP, Tor, Anomaly Detection)
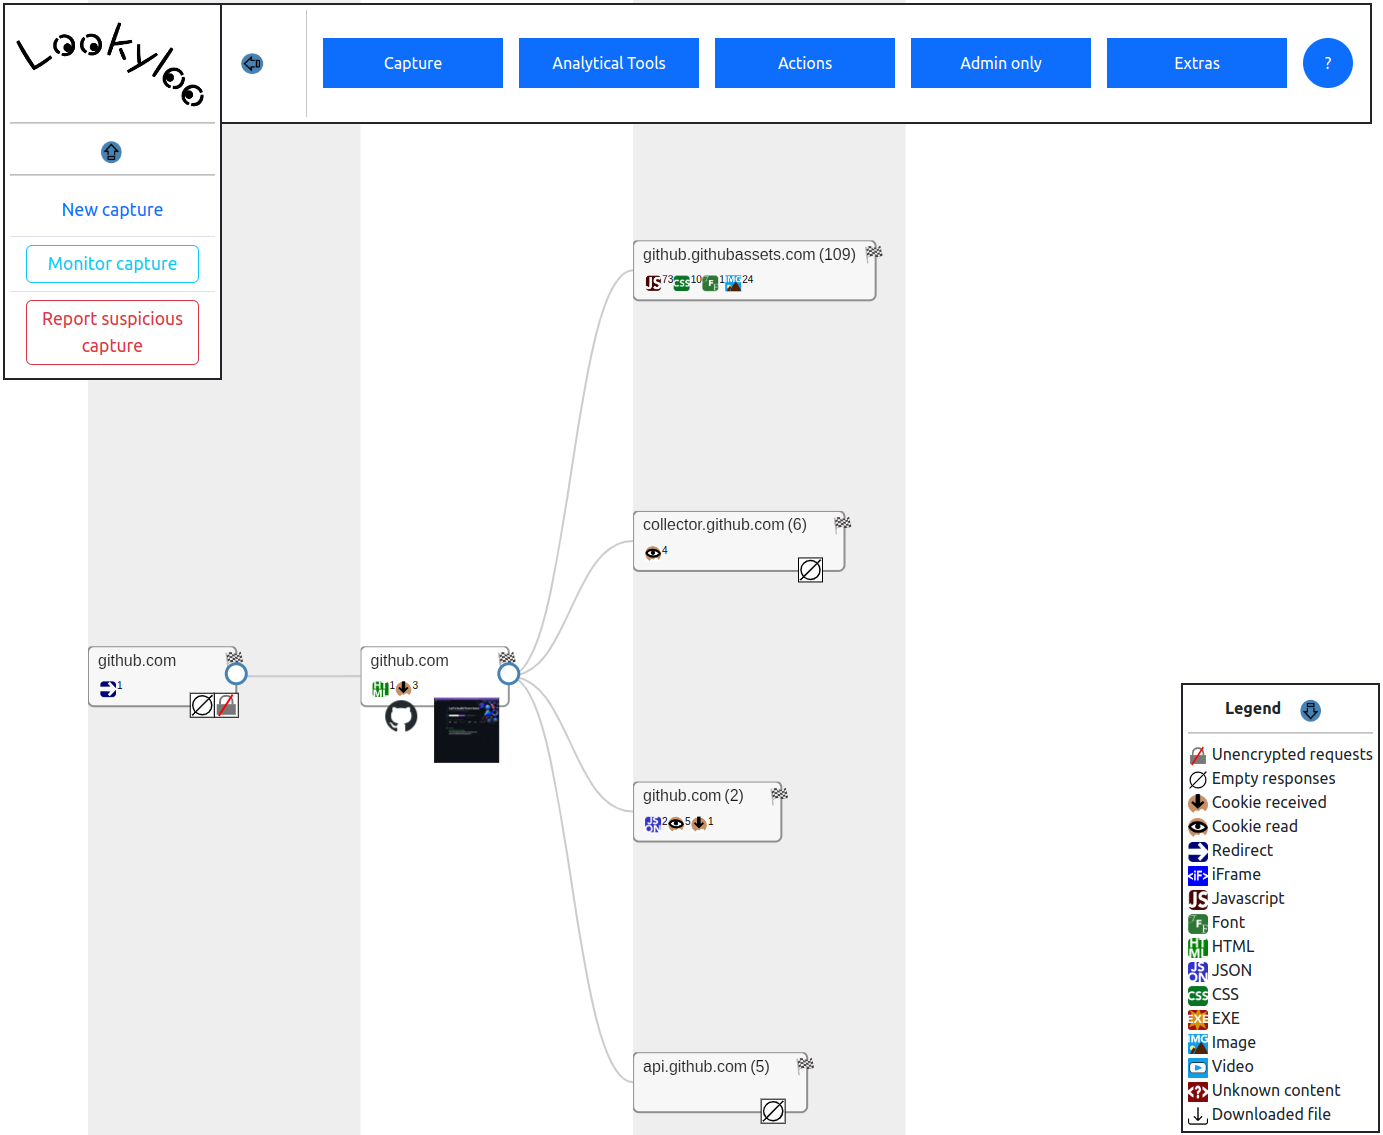
Lookyloo is a web interface that allows users to capture a website page and then display a tree of domains that call each other.
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application Security Testing (DAST).
:books:Translate the distinct technical blogs. Please star or watch. Welcome to join me.
Check Risk WAF is an all-in-one Web Application Firewall with Anti-Bot and Anti-DDoS protection at L3, L4, and L7. Available on-premises or as SaaS, it protects web apps against OWASP Top 10 attacks, CWE vulnerabilities, botnets, and DoS/DDoS. Free and unlimited for everyone, forever for personal, non-commercial use.
The most comprehensive Hack The Box writeup collection - 500+ machines, 400+ challenges, interactive knowledge graph, skill trees, attack path diagrams, ProLabs, Sherlocks, OSCP/CPTS/CRTO prep. Browse: momenbasel.github.io/htb-writeups
A free, open-source alternative to Burp Suite: an intercepting proxy and web app security testing suite with Repeater, Intruder, Collaborator and a built-in OWASP ZAP scanner. Linux, AGPL-3.0.
The complete hacking & penetration testing roadmap. From beginner to elite. 44,982 lines, 150+ Diagram across the roadmap: OPSEC, web security, Active Directory, binary exploitation, EDR evasion, and 0-day research. 300+ tools, 200+ MITRE techniques, C & Rust payloads, lab guides, books, courses, blogs, practice platforms, and AI security resources
A Burpsuite plugin (BApp) to aid in the detection of scripts being loaded from over 23000 malicious cryptocurrency mining domains (cryptojacking).
本项目通过大模型联动爬虫,检索Github上所有存有有价值漏洞信息与漏洞POC或规则信息的项目,并自动识别项目的目录结构、Readme信息后进行总结分析并分类,所汇总的项目可以帮助安全行业从业者收集漏洞信息、POC信息、规则等。
Open-source security suite for OSINT, web scanning, API testing, SIEM integration, and AI-powered analysis
Secure PHP Development — lab-driven study notes: modern PHP 8.2/8.3 through a full OWASP-mapped catalogue of PHP vulnerabilities with exploit-then-fix labs. CC BY 4.0.
A curated collection of 70+ free cybersecurity books organized by domain and difficulty (🟢 Beginner → 🟡 Intermediate → 🔴 Advanced). Structured learning paths for ethical hacking, penetration testing, exploit development, malware analysis, web security, and more. No paywall. Community maintained.
🎯 A structured 60-week penetration testing curriculum with 500+ free TryHackMe labs, OWASP Top 10 deep dives, tool mastery guides, and certification roadmaps. Three learning paths from zero to professional pentester. 2026 Edition; includes AI/LLM, Cloud & API security.
Free web security, SEO & AI-visibility (GEO) scan
Runs in the browser on Hugging Face