SafeLine
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
- 23k
- Go
- GPL-3.0
- 1 d ago
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
Stop half-done APIs! Cherrybomb is a CLI tool that helps you avoid undefined user behaviour by auditing your API specifications, validating them and running API security tests.
Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.
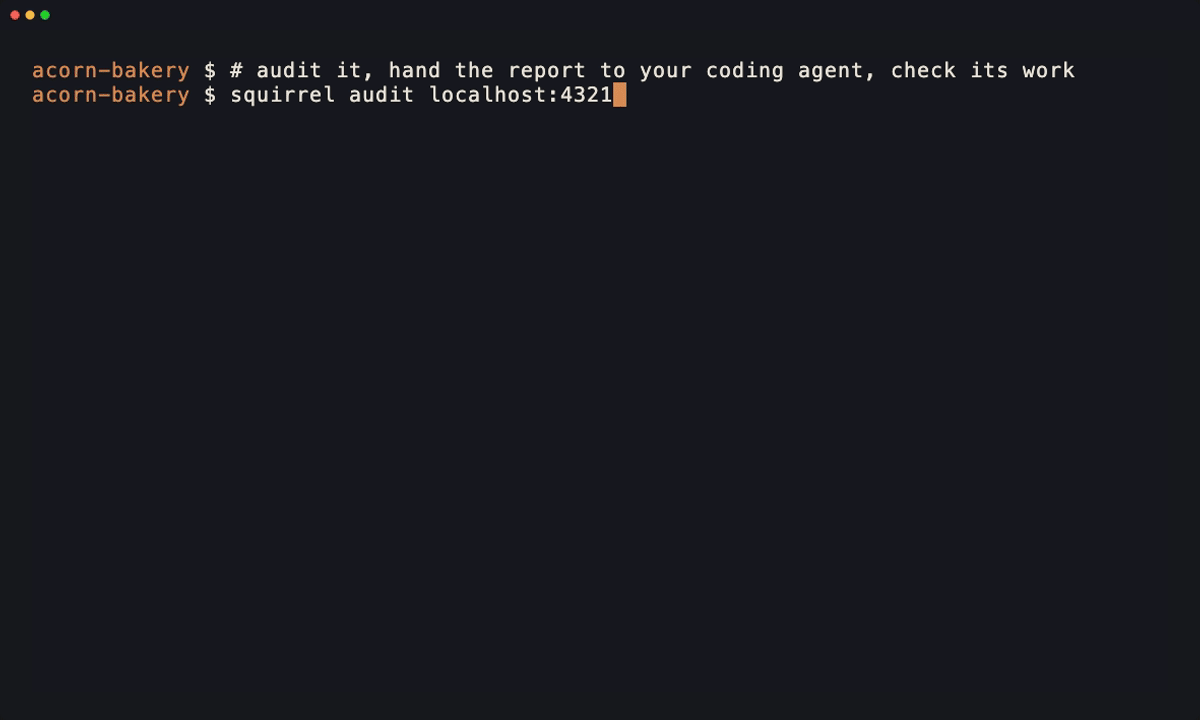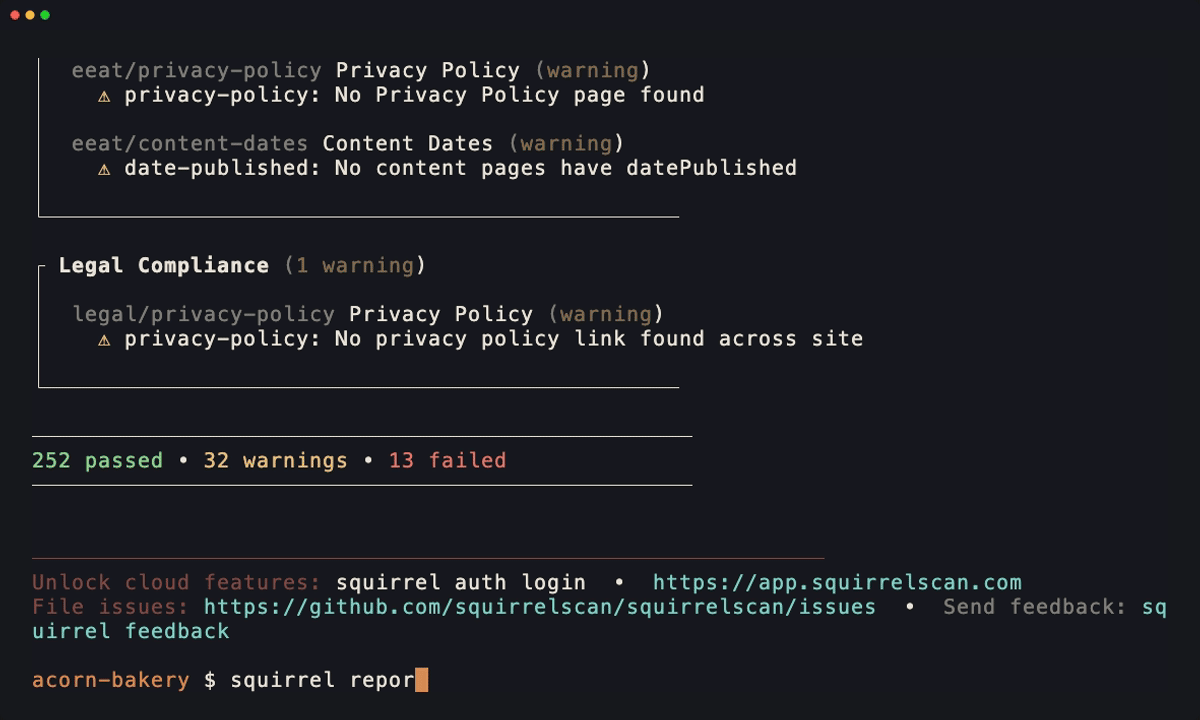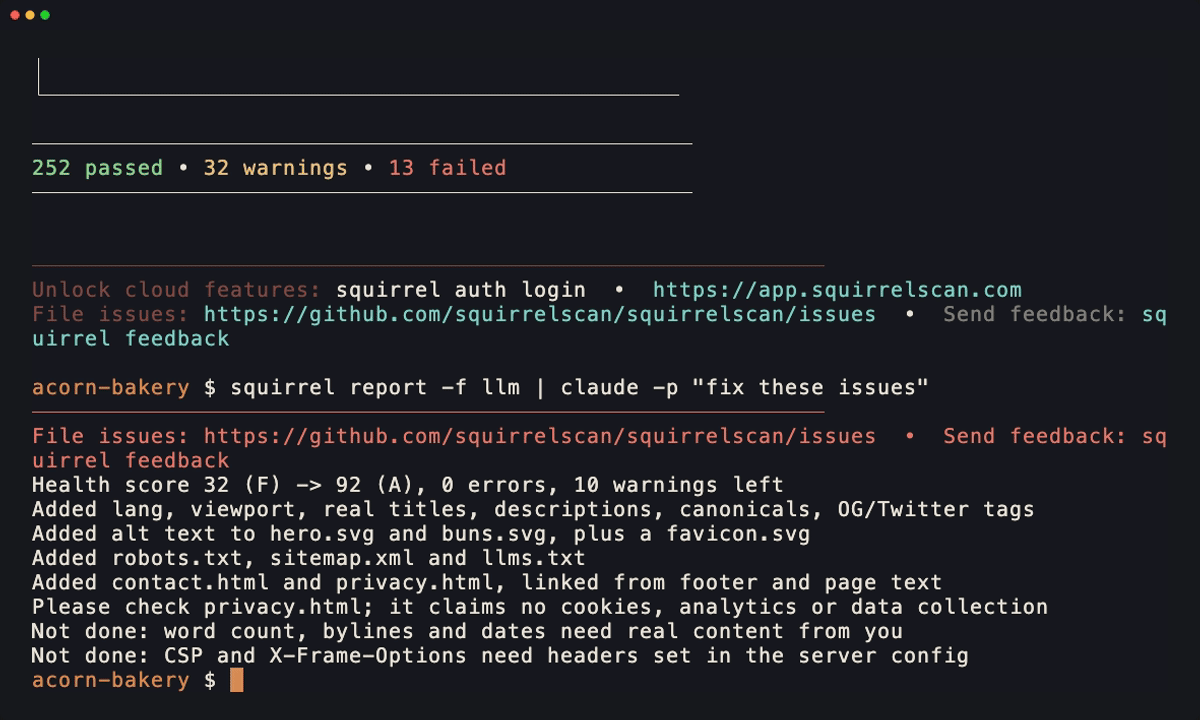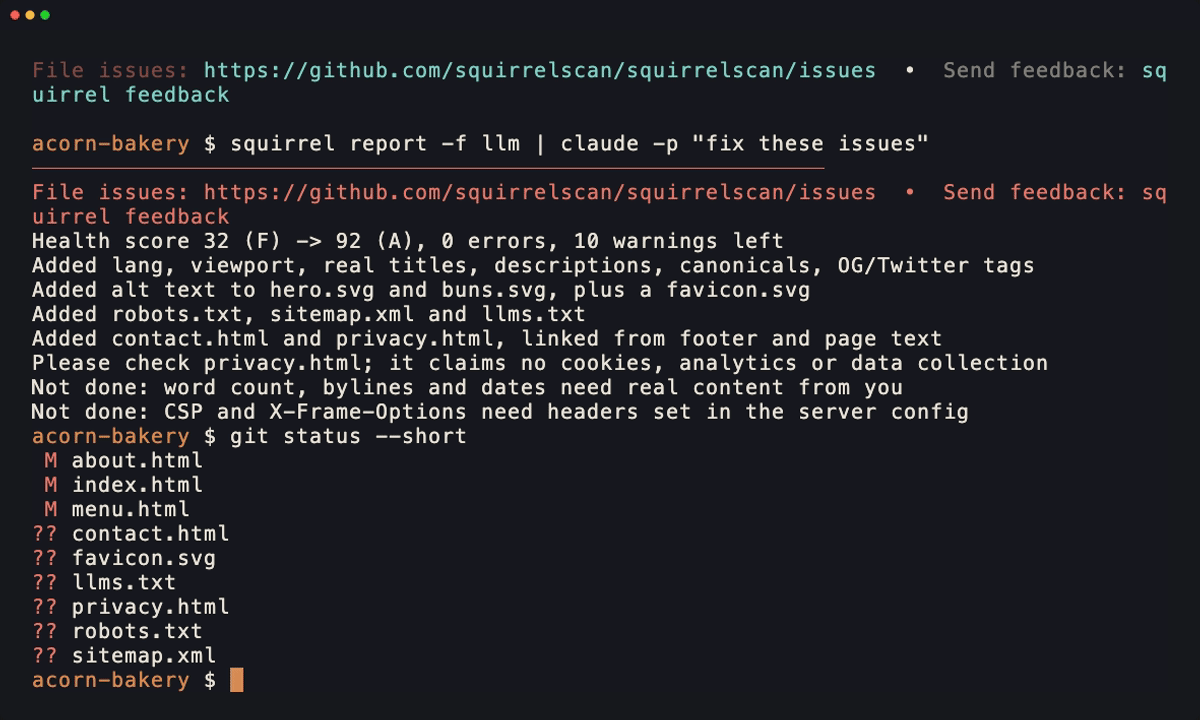
The website QA tool for your coding agent. 350+ audit rules across SEO, performance, security, accessibility and agent experience.
Check Risk WAF is an all-in-one Web Application Firewall with Anti-Bot and Anti-DDoS protection at L3, L4, and L7. Available on-premises or as SaaS, it protects web apps against OWASP Top 10 attacks, CWE vulnerabilities, botnets, and DoS/DDoS. Free and unlimited for everyone, forever for personal, non-commercial use.
HTTP client with built-in SSRF protection, compatible with Tesla and HTTPoison
This Extension provides a Passive and Active Scan Check that detects V1 UUIDs and attempts to find other potentially valid ones.
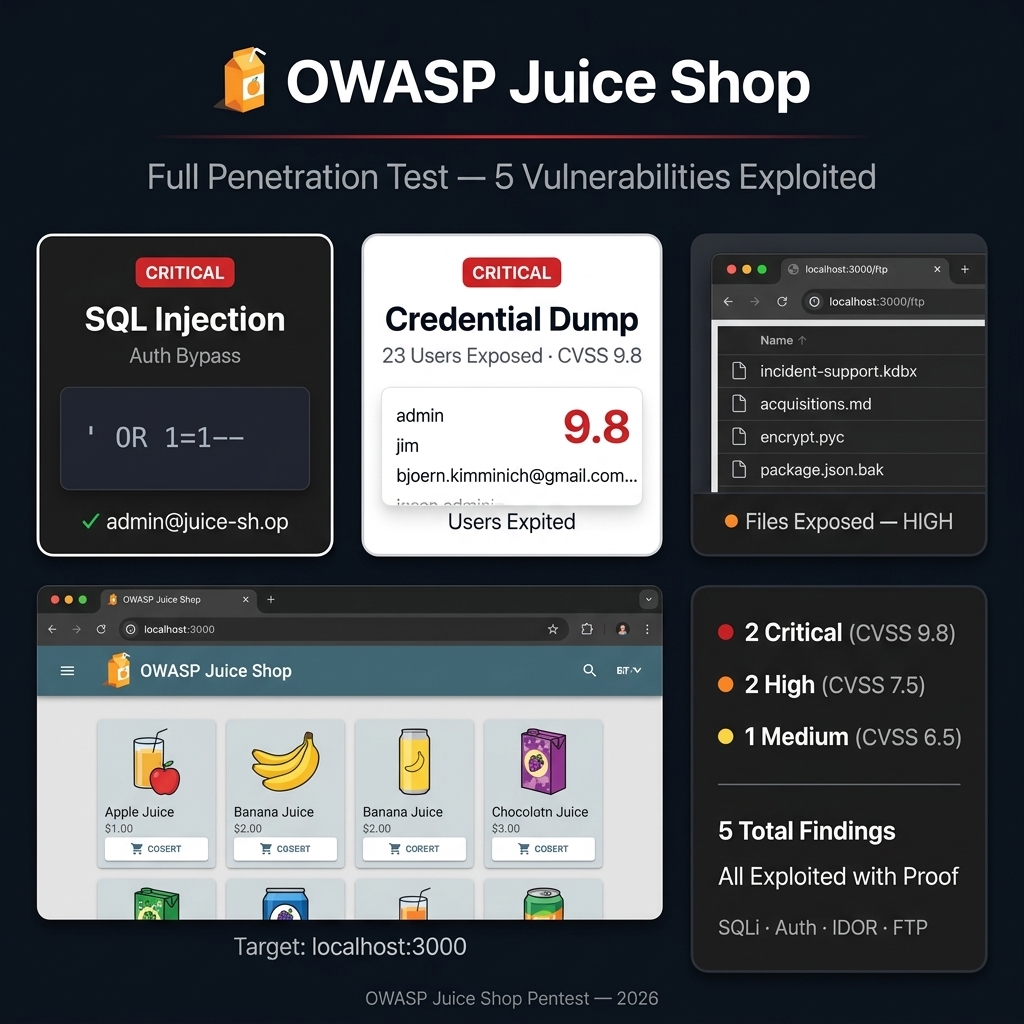
🧃 Full penetration test on OWASP Juice Shop — 5 vulnerabilities exploited (SQL Injection, Auth Bypass, Broken Access Control, File Exposure). All findings include working payloads and proof of exploitation.
Cybersecurity research, vulnerability writeups, methodologies, and hands-on security learning.
An ML-based system to detect phishing websites using URL and domain analysis. Includes Source Code, PPT, Synopsis, Report, Documents, Base Research Paper & Video tutorials.