PayloadsAllTheThings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
- 83k
- Python
- MIT
- 3 wk ago
This script is used to bypass DLL Hooking using a fresh mapped copy of ntdll file, patch the ETW and trigger a shellcode with process hollowing
Repo ProcessusT/UnhookingDLL, read from GitHub 1 min ago. ProcessusT has not joined Take My Repo.
ProcessusT/UnhookingDLL is a public repo on GitHub by ProcessusT. This script is used to bypass DLL Hooking using a fresh mapped copy of ntdll file, patch the ETW and trigger a shellcode with process hollowing. It declares no license on GitHub. Public does not mean open source: without a license, nobody is granted the right to reuse it. It is written mainly in C++, has 74 stars and last changed on 2024-02-11. Nobody has reviewed it on Take My Repo yet, which says nothing about its quality. Read from GitHub on 2026-11-21.
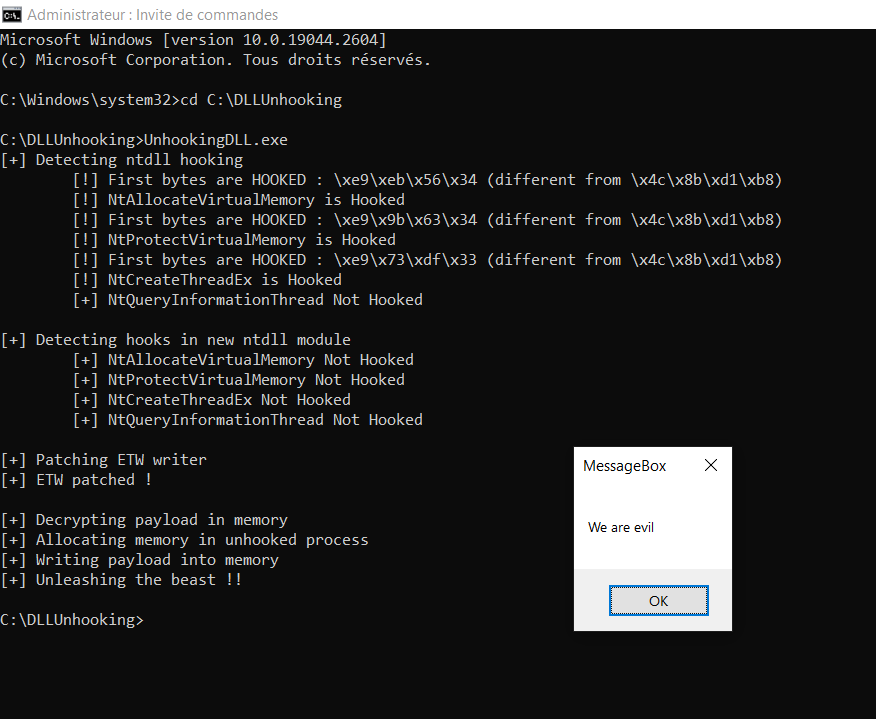
ProcessusT/UnhookingDLL is a public repo on GitHub by ProcessusT. This script is used to bypass DLL Hooking using a fresh mapped copy of ntdll file, patch the ETW and trigger a shellcode with process hollowing.
It declares no license on GitHub. Public does not mean open source: without a license, nobody is granted the right to reuse it.
Its maker has not tagged a system, so it is unknown here. Its README says what it needs.
Open "Take it" on its page: Take My Repo writes an install plan for your machine and hands it to your AI agent (Claude Code, Codex or Cursor), which asks you before each step. Take My Repo has not tested it on any machine.
Its last change on GitHub was on 2024-02-11. Take My Repo does not judge from that whether it is maintained.
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
Nobody has reviewed it on Take My Repo yet, which says nothing about its quality.
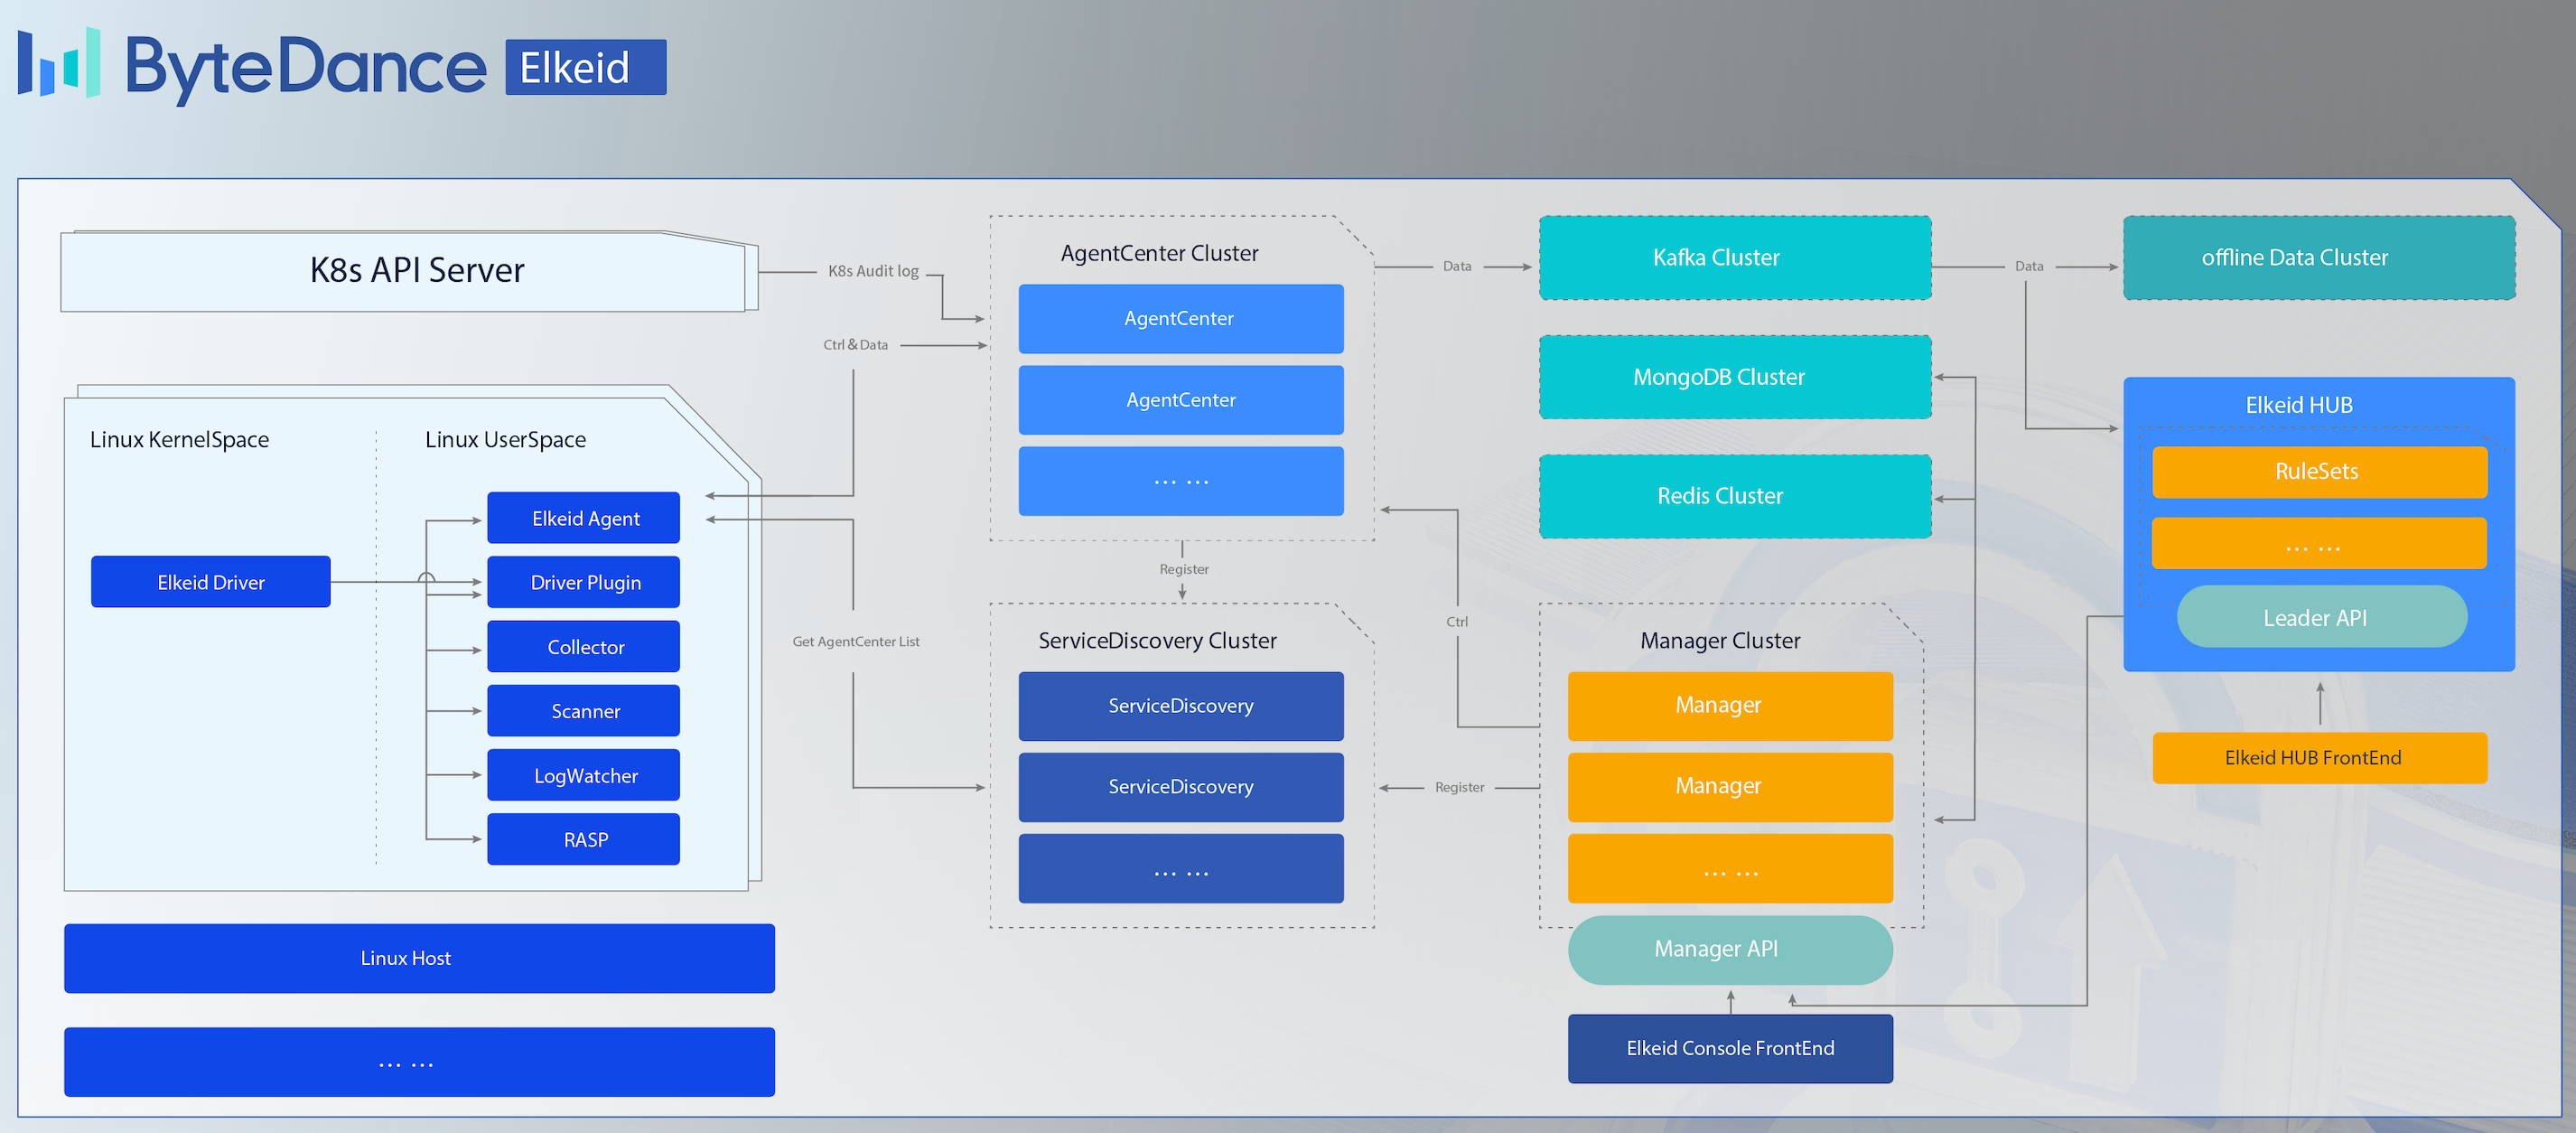
Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It is derived from ByteDance's internal best practices.
An advanced profiler for .NET and Native Applications on Windows, macOS and Linux, with Agentic integration.
Stealthy, Linux-first multi-operator C2 with a self-healing mesh, in-memory execution, AI-driven MCP assistant, and autonomous evasion loop.
Open-source Windows EDR that detects RATs and infostealers in real time, with ATT&CK-mapped rules and triage.
Hekatomb is a python script that connects to LDAP directory to retrieve all computers and users informations. Then it will download all DPAPI blob of all users from all computers and uses Domain backup keys to decrypt them.
Bruteforce DPAPI encrypted MasterKey File from Windows Credentials Manager
Un dropper de payload indétectable qui désactive l'antivirus Windows Defender puis paramètre un fichier batch à l'ouverture de session de l'utilisateur courant pour télécharger netcat et initier une connexion de type reverse shell vers un serveur C2.
Tool to enumerate ESET hooked functions by parsing the ebehmoni.dll module
Autonomous red team implementation allowing sound capture and broadcast through an untraceable front-end server to the attacker's station