Hacking-Windows
A FREE Windows C development course where we will learn the Win32API and reverse engineer each step utilizing IDA Free in both an x86 and x64 environment.
- 1.6k
- C
- Apache-2.0
- 4 d ago
A FREE Windows C development course where we will learn the Win32API and reverse engineer each step utilizing IDA Free in both an x86 and x64 environment.
IDA Pro plugin with a rich set of features: decryption, deobfuscation, patching, lib code recognition and various pseudocode transformations
🔥🔥🔥微信公众号:Cydiapps🔥🔥🔥 => Cydia插件 Logos语言 开发Tweak.xm Cydia Substrate 注入dylib iOS逆向工程开发 越狱Jailbreak deb插件 - fishhook / Frida / iOSOpenDev / Cycript / MachOView / IDA / Hopper Disassembler / MonkeyDev / Class-dump / Theos / Reveal / Dumpdecryptd / FLEX / 汇编Assembly / CaptainHook / lldb/LLVM/XNU/Darwin/iOS Reverse
Find JNI function signatures in APK and apply to reverse-engineering tools.
A FREE comprehensive online Go hacking tutorial utilizing the x64, ARM64 and ARM32 architectures going step-by-step into the world of reverse engineering Golang from scratch.
x64dbg utility for linker map files, diff files, PEiD/IDA signatures, and code signature generation.
A FREE comprehensive online Rust hacking tutorial utilizing the x64, ARM64 and ARM32 architectures going step-by-step into the world of reverse engineering Rust from scratch.
Julia interface to Sundials, including a nonlinear solver (KINSOL), ODEs (CVODE and ARKODE), and DAEs (IDA)
VRChat IL2CPP deobfuscation pipeline — Unity 6 (6000.0.60f1) baseline. Reverse MethodInfo enumeration, 64K classes / 570K methods / 188K fields, reproducible naming.
Swift implementation of the Sliding Puzzle game with Iterative Deepening A* AI Solver.
Hex-Rays Decompiler plugin for better code navigation. plugin for IDA Pro.
many of ida pro idb database for game hacking and reverse analysis engineering.good luck.
idaemu is an IDA Pro Plugin - use for emulating code in IDA Pro.update for ida pro 7.7
Finds all first occurring string references near another reference
Dart AOT snapshot analyzer: exports blutter-compatible symbols and structs for IDA / radare2 / Frida, and decompiles functions into dart-analyze-clean Dart. Desktop and real-device mobile (compressed pointers), Dart 2.7-3.14. No Dart SDK, never runs the target.
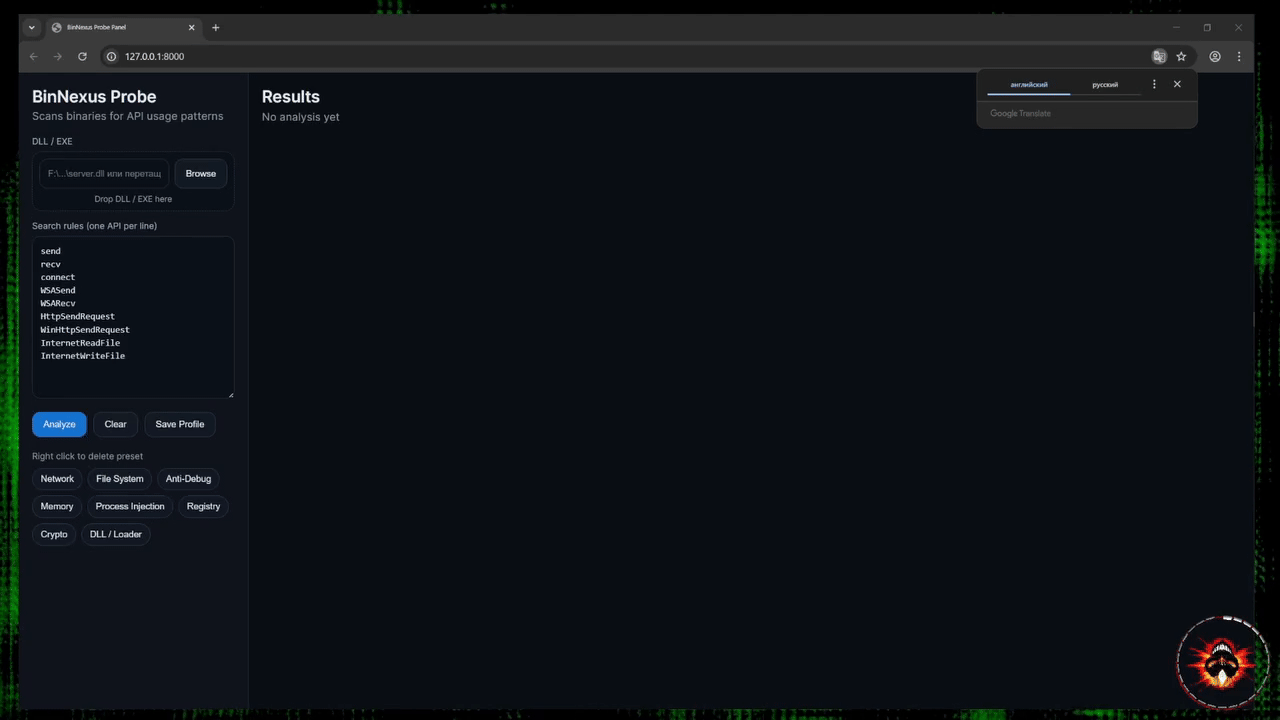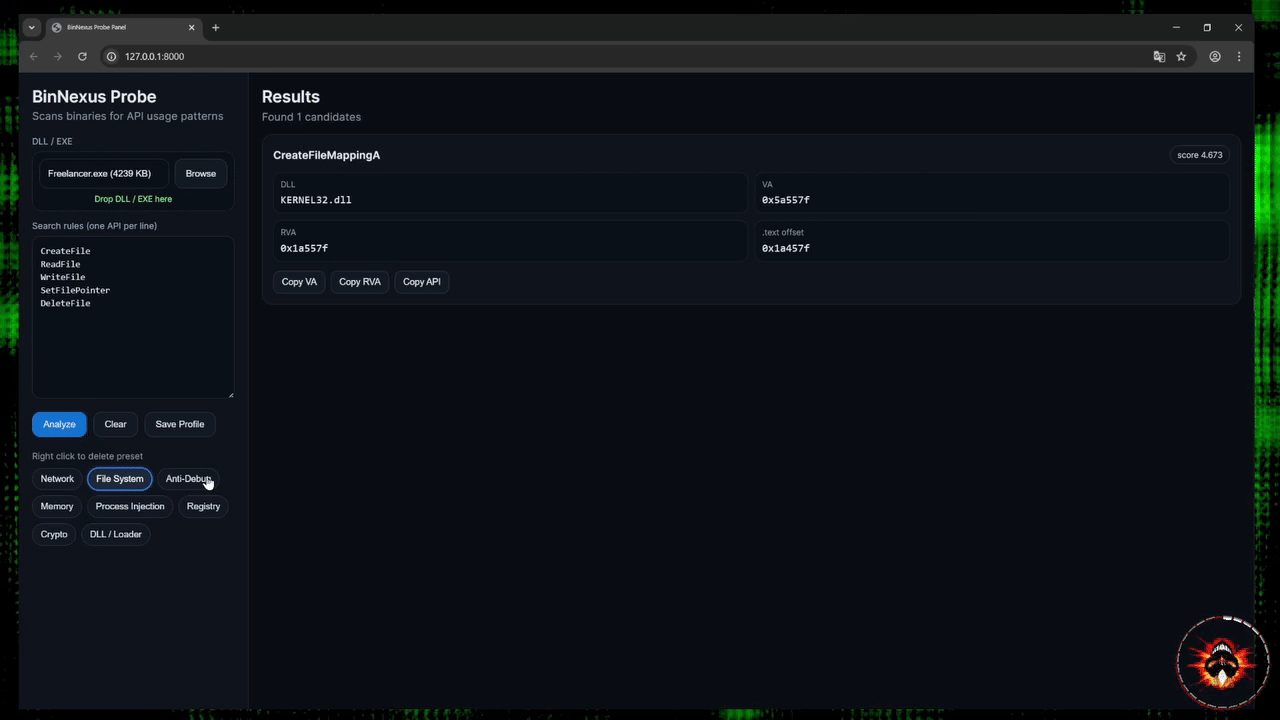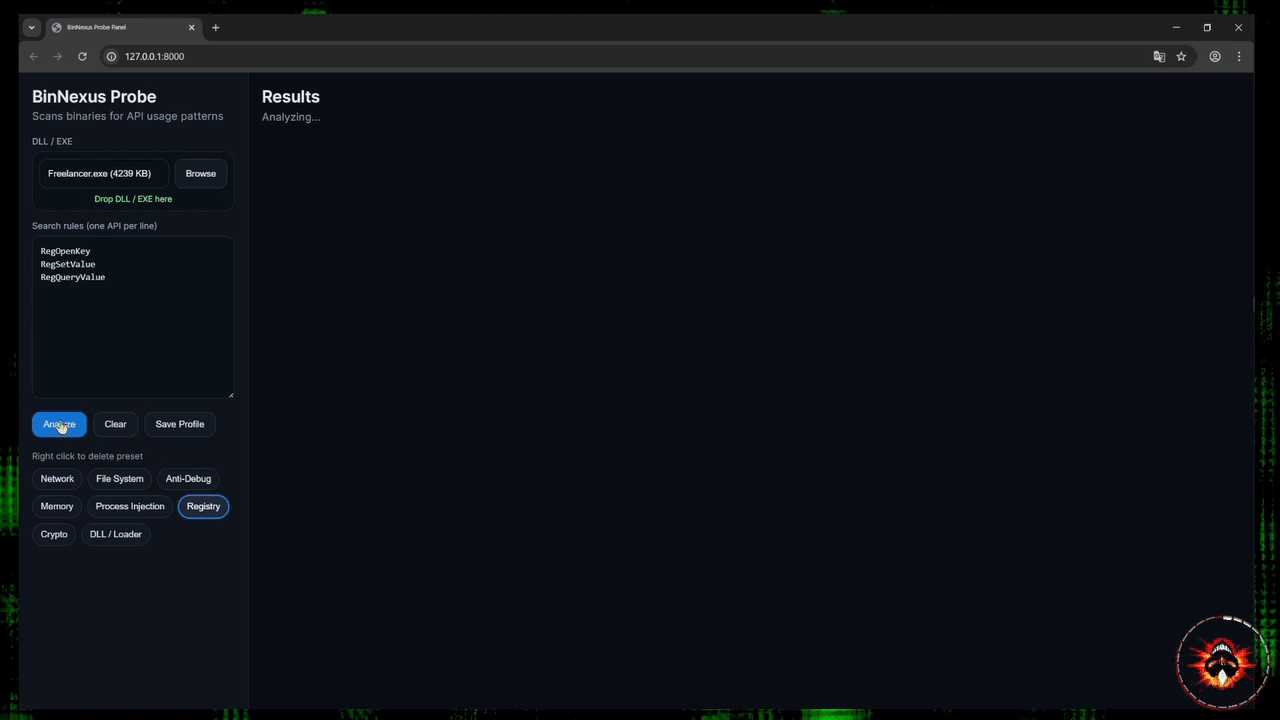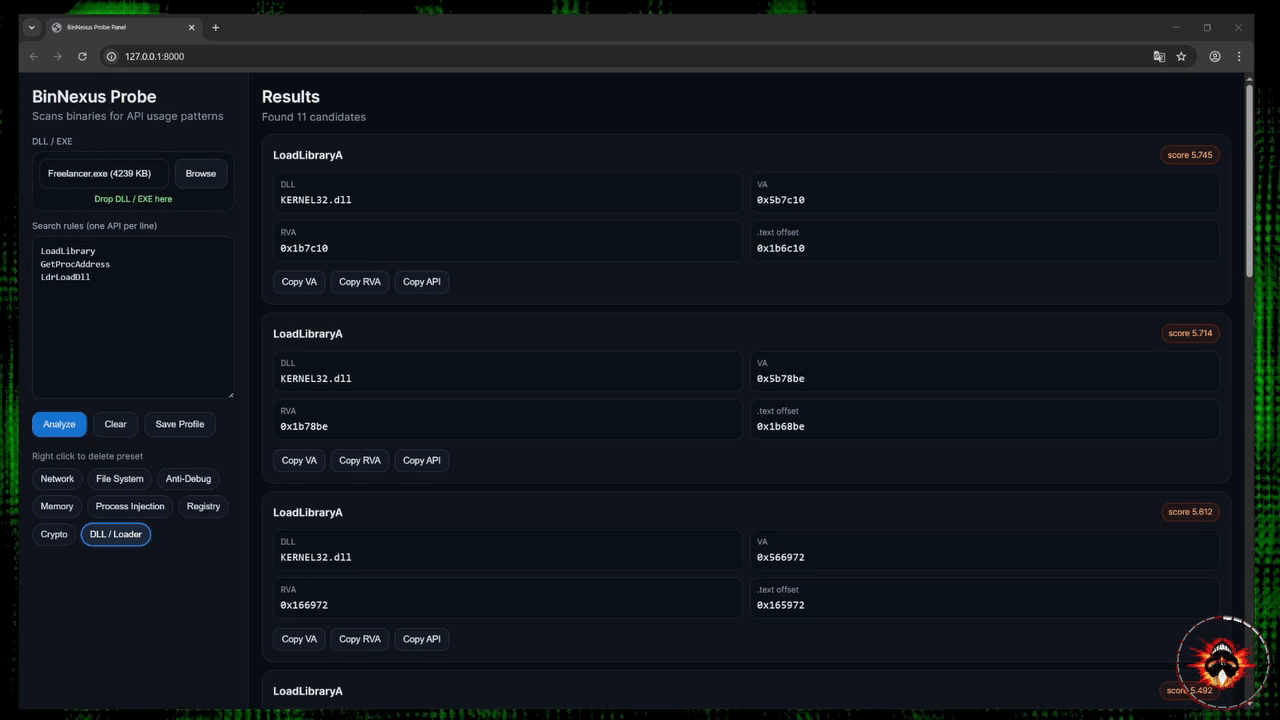
Is a fast API-based binary probing tool designed for quick behavioral inspection of executables and DLLs.
winhex_diff_viewer plugin for ida pro .IDA Plugin.
ida_all_xrefs_from_viewer-plugin-for-ida-pro , ida plugin.
ida_all_xrefs_to_viewer-plugin-for-ida-pro,ida plugin
Operand Analysis with IDA Pro: per-operand read/write status, operand type, operand id.
Portable, evidence-first AI-agent skill for lawful reverse engineering with REA CLI/MCP workflows.