strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
- 77k
- Python
- Apache-2.0
- 2 d ago
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
Shannon is an AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes real exploits to prove vulnerabilities before they reach production.
817 structured cybersecurity skills for AI agents · Mapped to 6 frameworks: MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, D3FEND, NIST AI RMF & MITRE F3 (Fight Fraud) · agentskills.io standard · Works with Claude Code, GitHub Copilot, Codex CLI, Cursor, Gemini CLI & 20+ platforms · 29 security domains · Apache 2.0
Fully autonomous AI Agents system capable of performing complex penetration testing tasks
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints and cloud workloads.
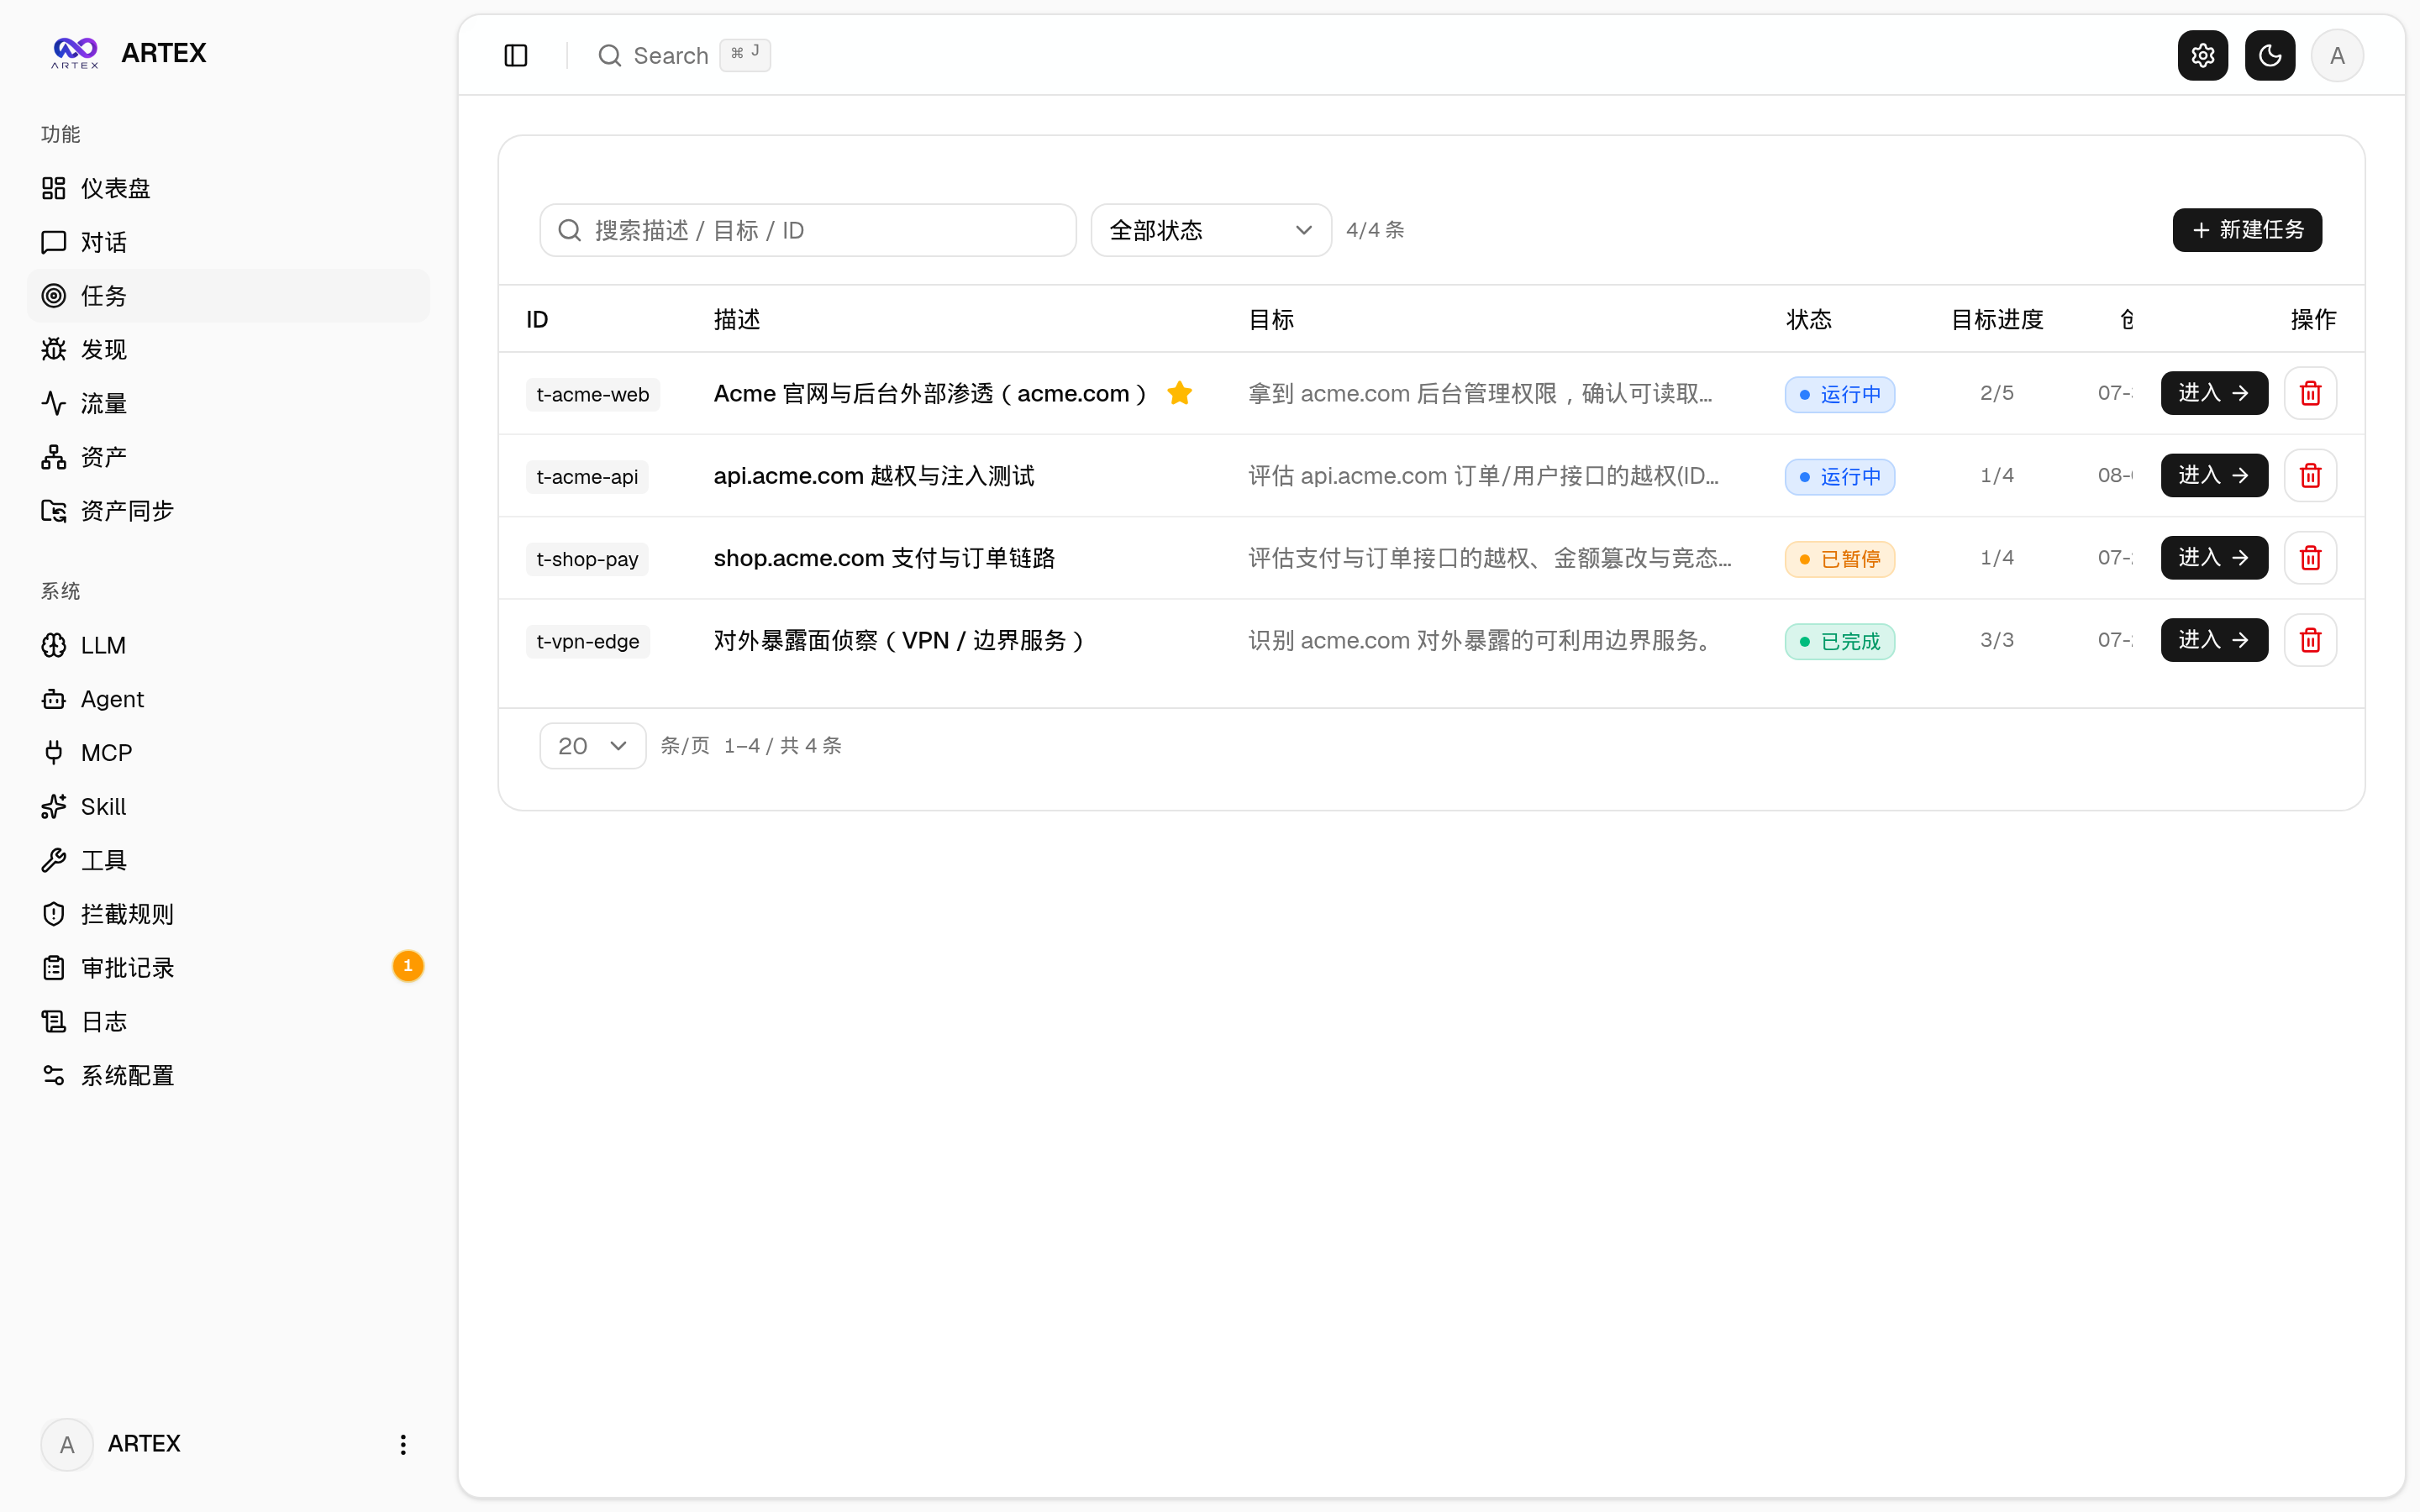
ARTEX - AI autonomous penetration testing system (English translation; upstream: Autumn-27/ARTEX, AGPL-3.0)
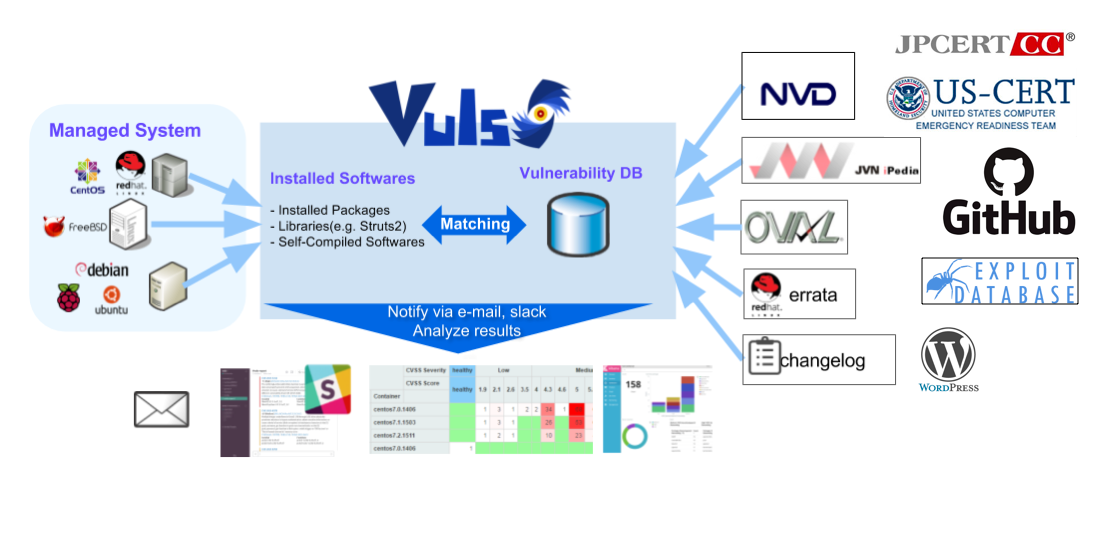
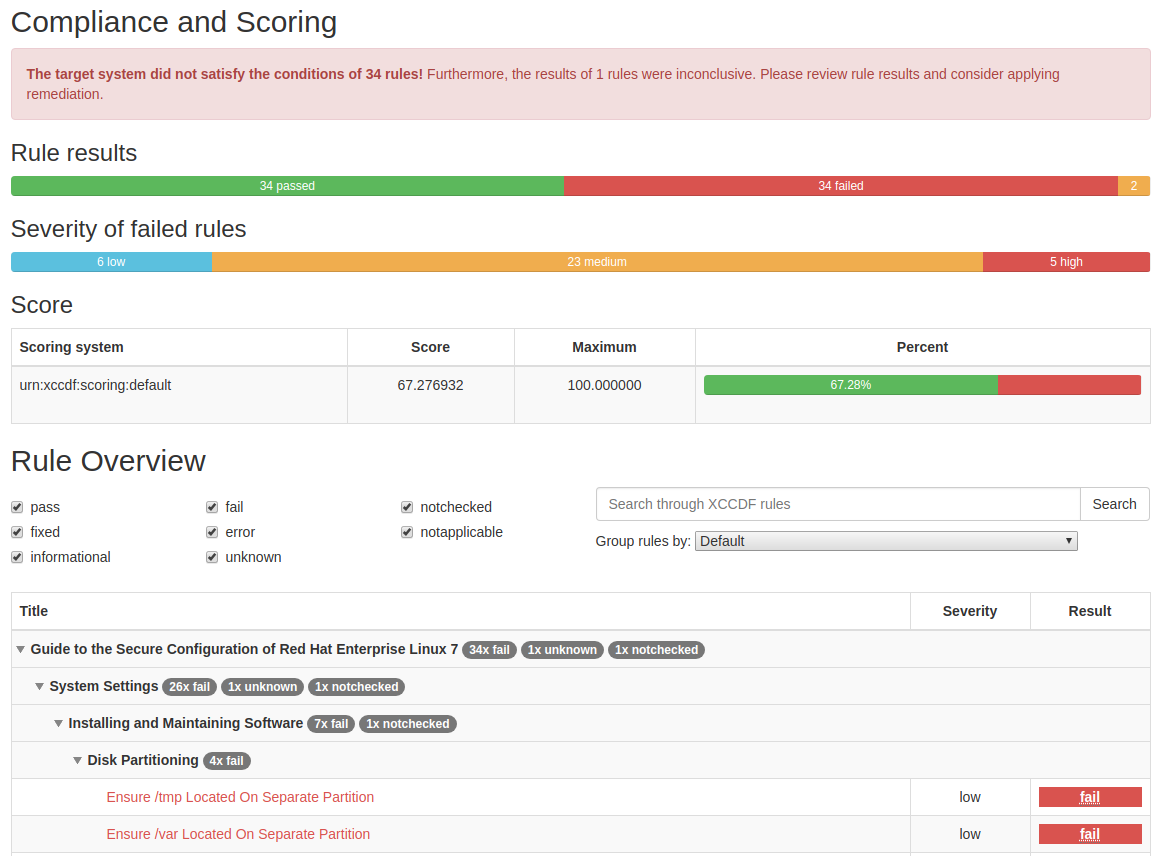
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
The Ultimate Open-Source Security Arsenal for Hackers, Enterprises, and AI Agents——面向极客、企业与 AI 智能体的全域开源网络安全工具矩阵
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin America, used worldwide.
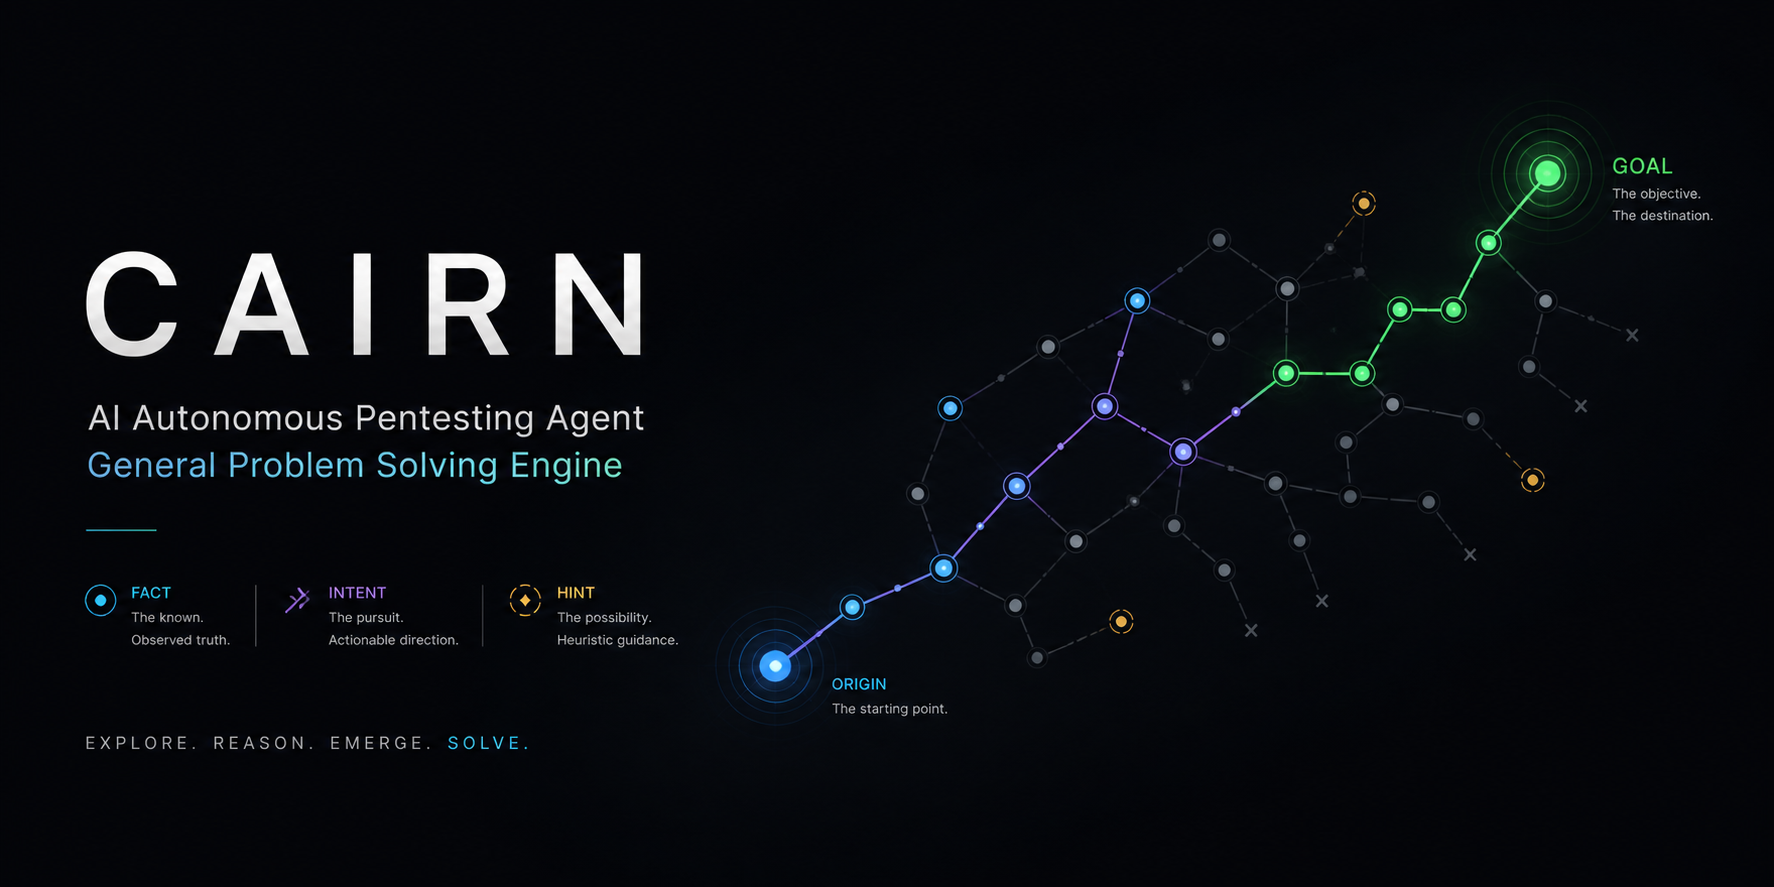
Cairn is a general-purpose AI state-space search engine, validated first on autonomous penetration testing. Sometimes misspelled as Carin.
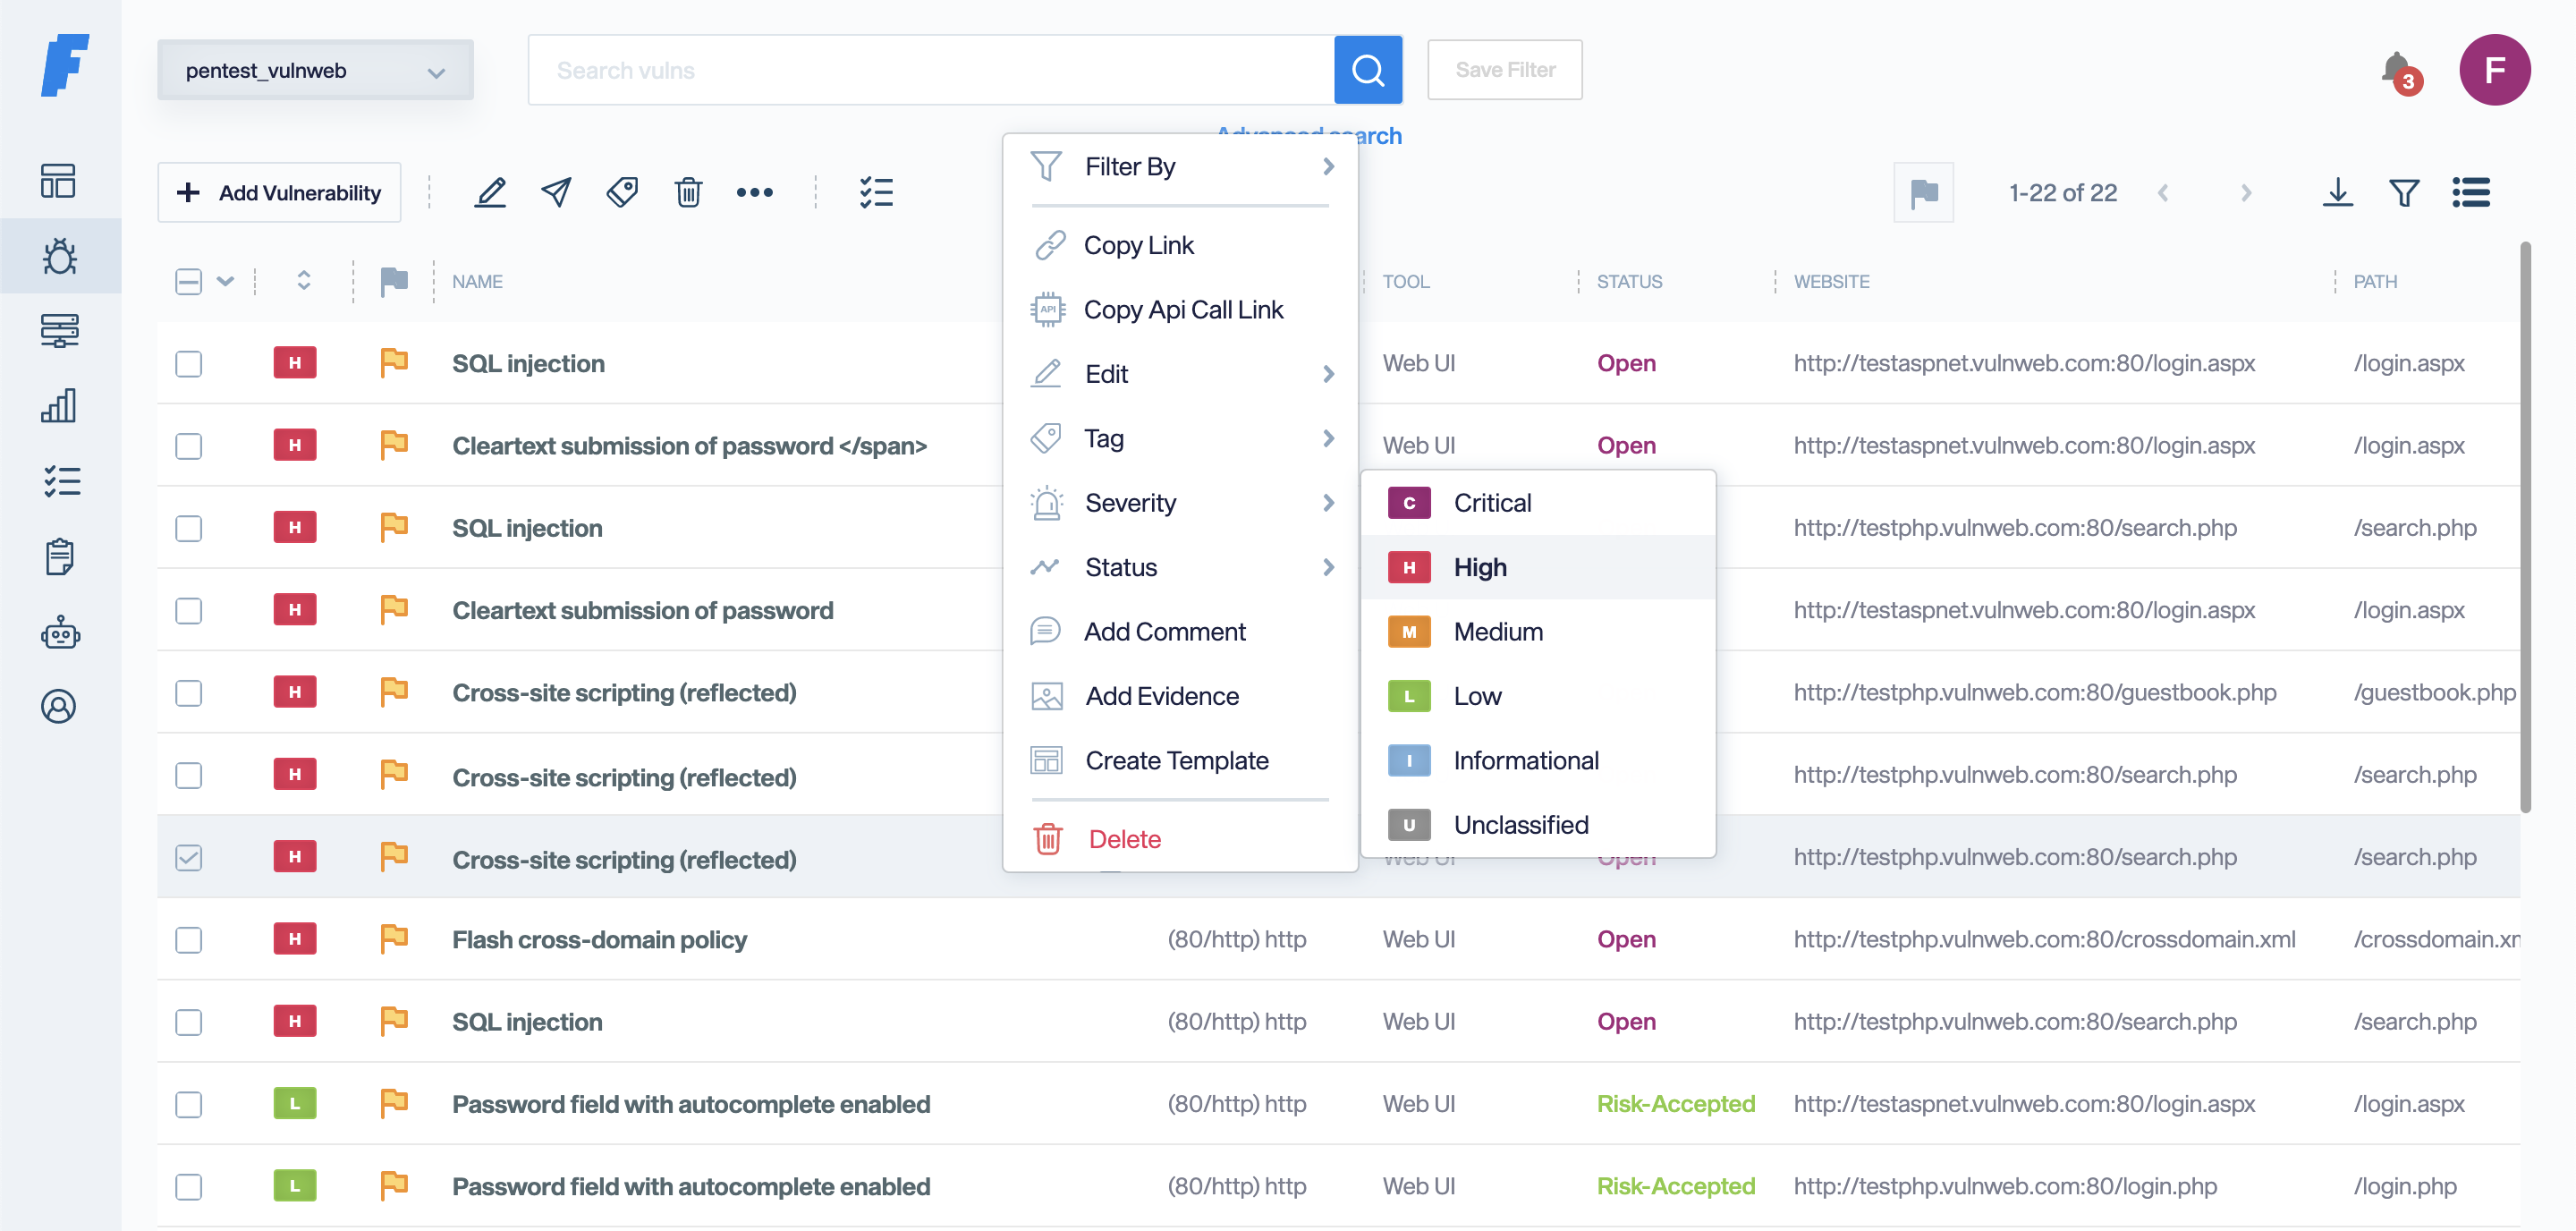
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
Dependency-Track is an intelligent Component Analysis platform that allows organizations to identify and reduce risk in the software supply chain.
Open-source AI-powered offensive security harness for automated penetration testing.
Hayabusa (隼) is a sigma-based threat hunting and fast forensics timeline generator for Windows event logs.
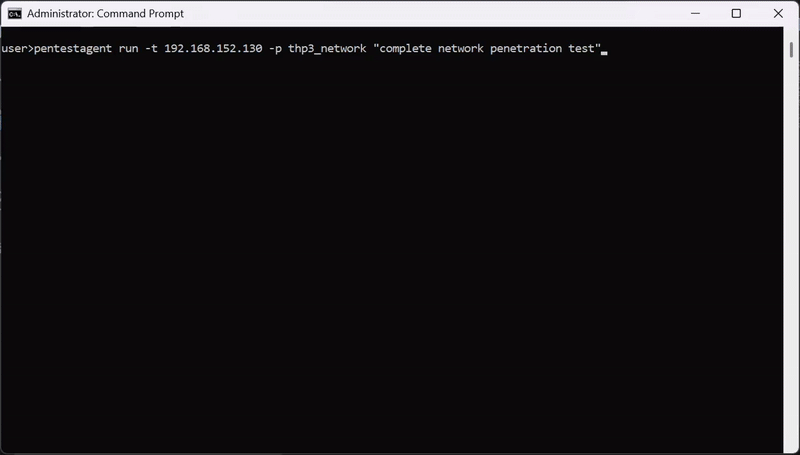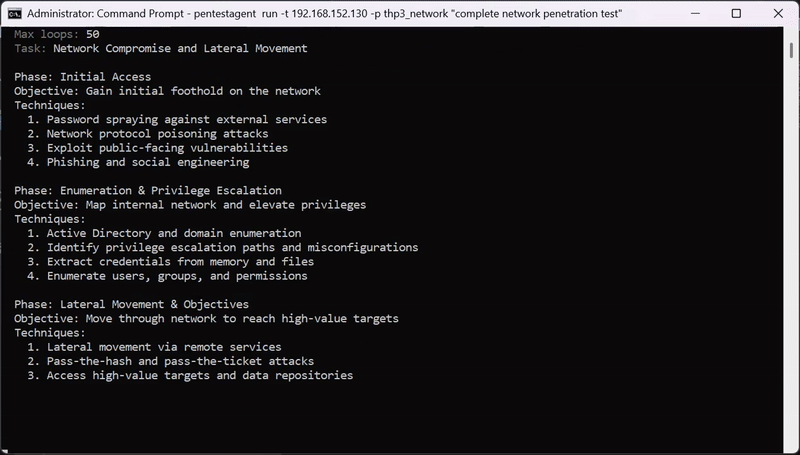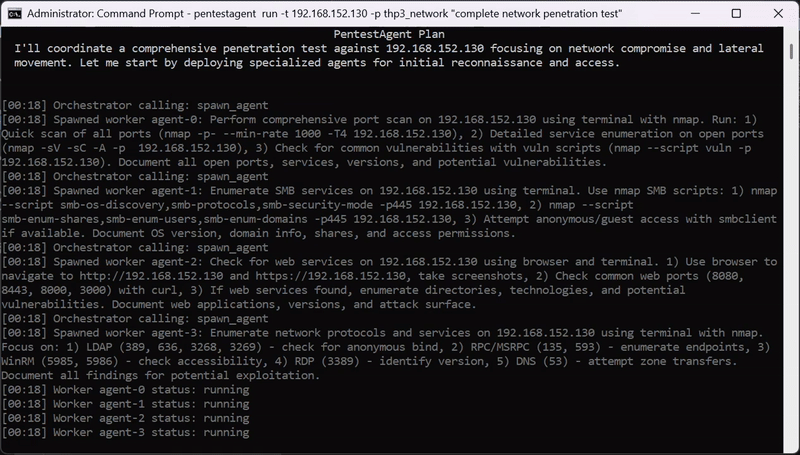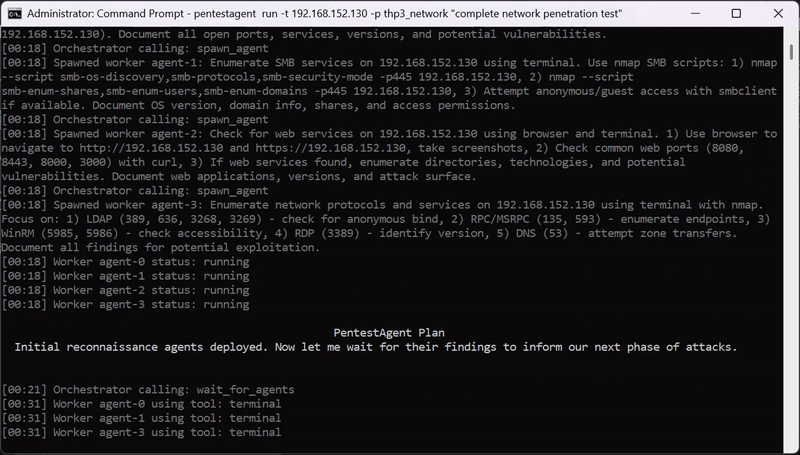
PentestAgent is an AI agent framework for black-box security testing, supporting bug bounty, red-team, and penetration testing workflows.
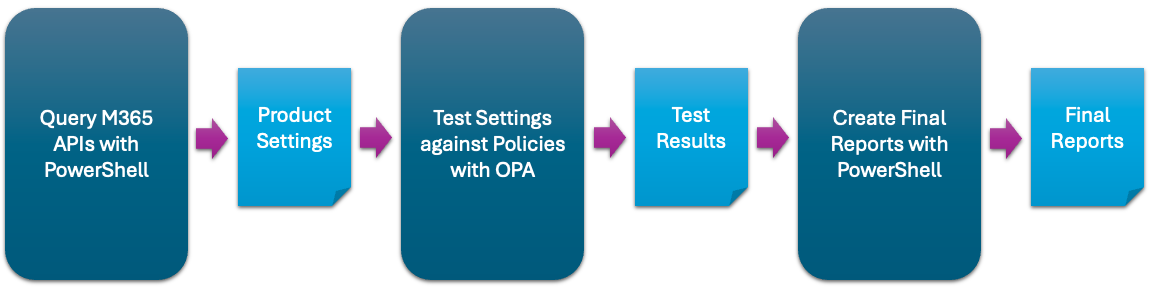
Automation to assess the state of your M365 tenant against CISA's baselines
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements, analyze recon, research exploits, build detections, audit STIGs, and write reports.
Open-source, self-hosted AI vulnerability research tool that orchestrates agents to find and validate security issues in code.
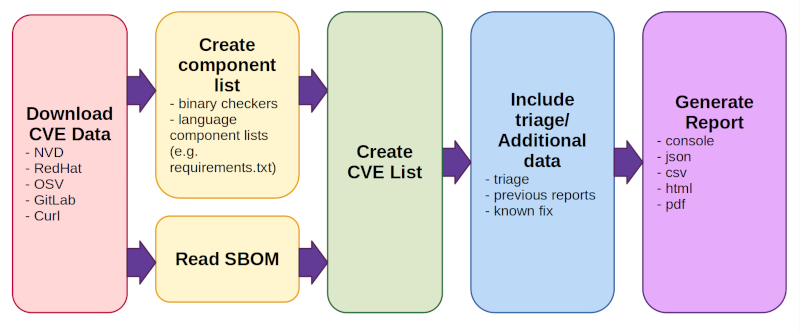
The CVE Binary Tool helps you determine if your system includes known vulnerabilities. You can scan binaries for over 350 common, vulnerable components (openssl, libpng, libxml2, expat and others), or if you know the components used, you can get a list of known vulnerabilities associated with an SBOM or a list of components and versions.
Security Orchestration, Automation and Response (SOAR) Platform. 安全编排与自动化响应平台,无需编写代码的安全自动化,使用 SOAR 可以让团队工作更加高效
LuaN1aoAgent is a fully autonomous AI-driven penetration testing agent powered by graph-based cognitive reasoning.
PentestCode - Multi-agent AI penetration testing system with persistent engagement state, strategic coordination, and parallel autonomous operations.
Reconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from reconnaissance through execution and reporting. With built-in command automation, output parsing, and AI‑assisted summaries, it delivers faster, more structured, and high‑quality security assessments.
Security automation with n8n ideas: 100+ Red/Blue/AppSec workflows, integrations, and ready-to-run playbooks.
A command-line tool to get valuable information out of AWS CloudTrail