redteam

PayloadsAllTheThings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
- 83k
- Python
- MIT
- 3 wk ago


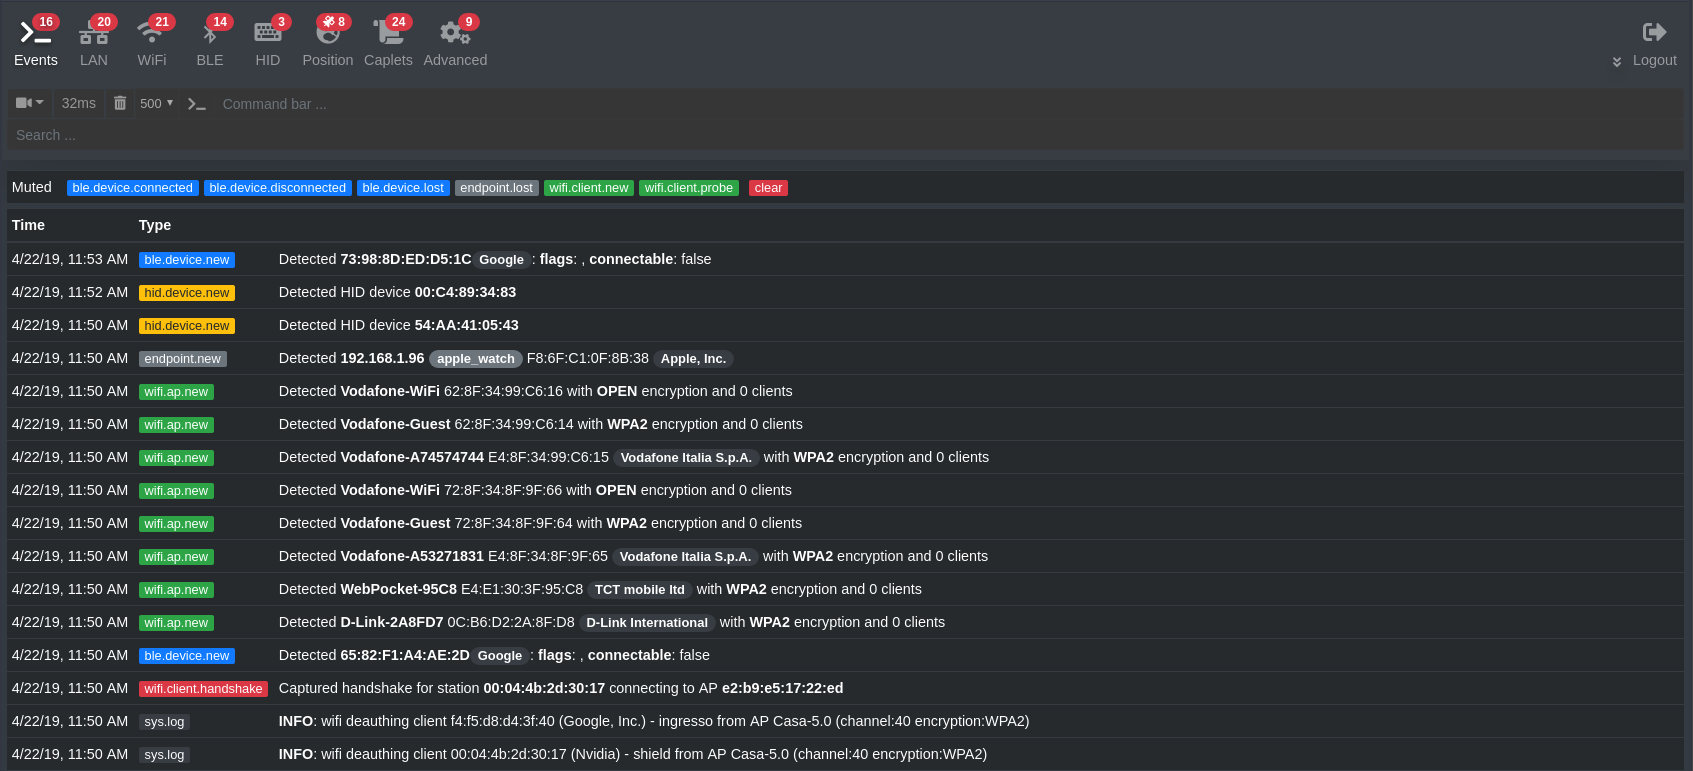
bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
- 20k
- Go
- 8 d ago


awesome-hacker-search-engines
A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more
- 12k
- Shell
- MIT
- 6 d ago


Claude-Red
claude-red is a curated library of offensive security skills designed for the Claude skills system. Each skill is a structured SKILL.md file that primes Claude with expert-level methodology for a specific attack surface — from SQLi to shellcode, EDR evasion to exploit development.
- 11k
- Python
- MIT
- 2 d ago


nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
- 10k
- PowerShell
- 3 y ago

kubernetes-goat
Kubernetes Goat is a "Vulnerable by Design" cluster environment to learn and practice Kubernetes security using an interactive hands-on playground 🚀
- 6k
- HTML
- MIT
- 7 mo ago

T3MP3ST
autonomous red teaming platform; multi-agent offensive-security meta-harness
- 7.1k
- TypeScript
- AGPL-3.0
- 2 mo ago




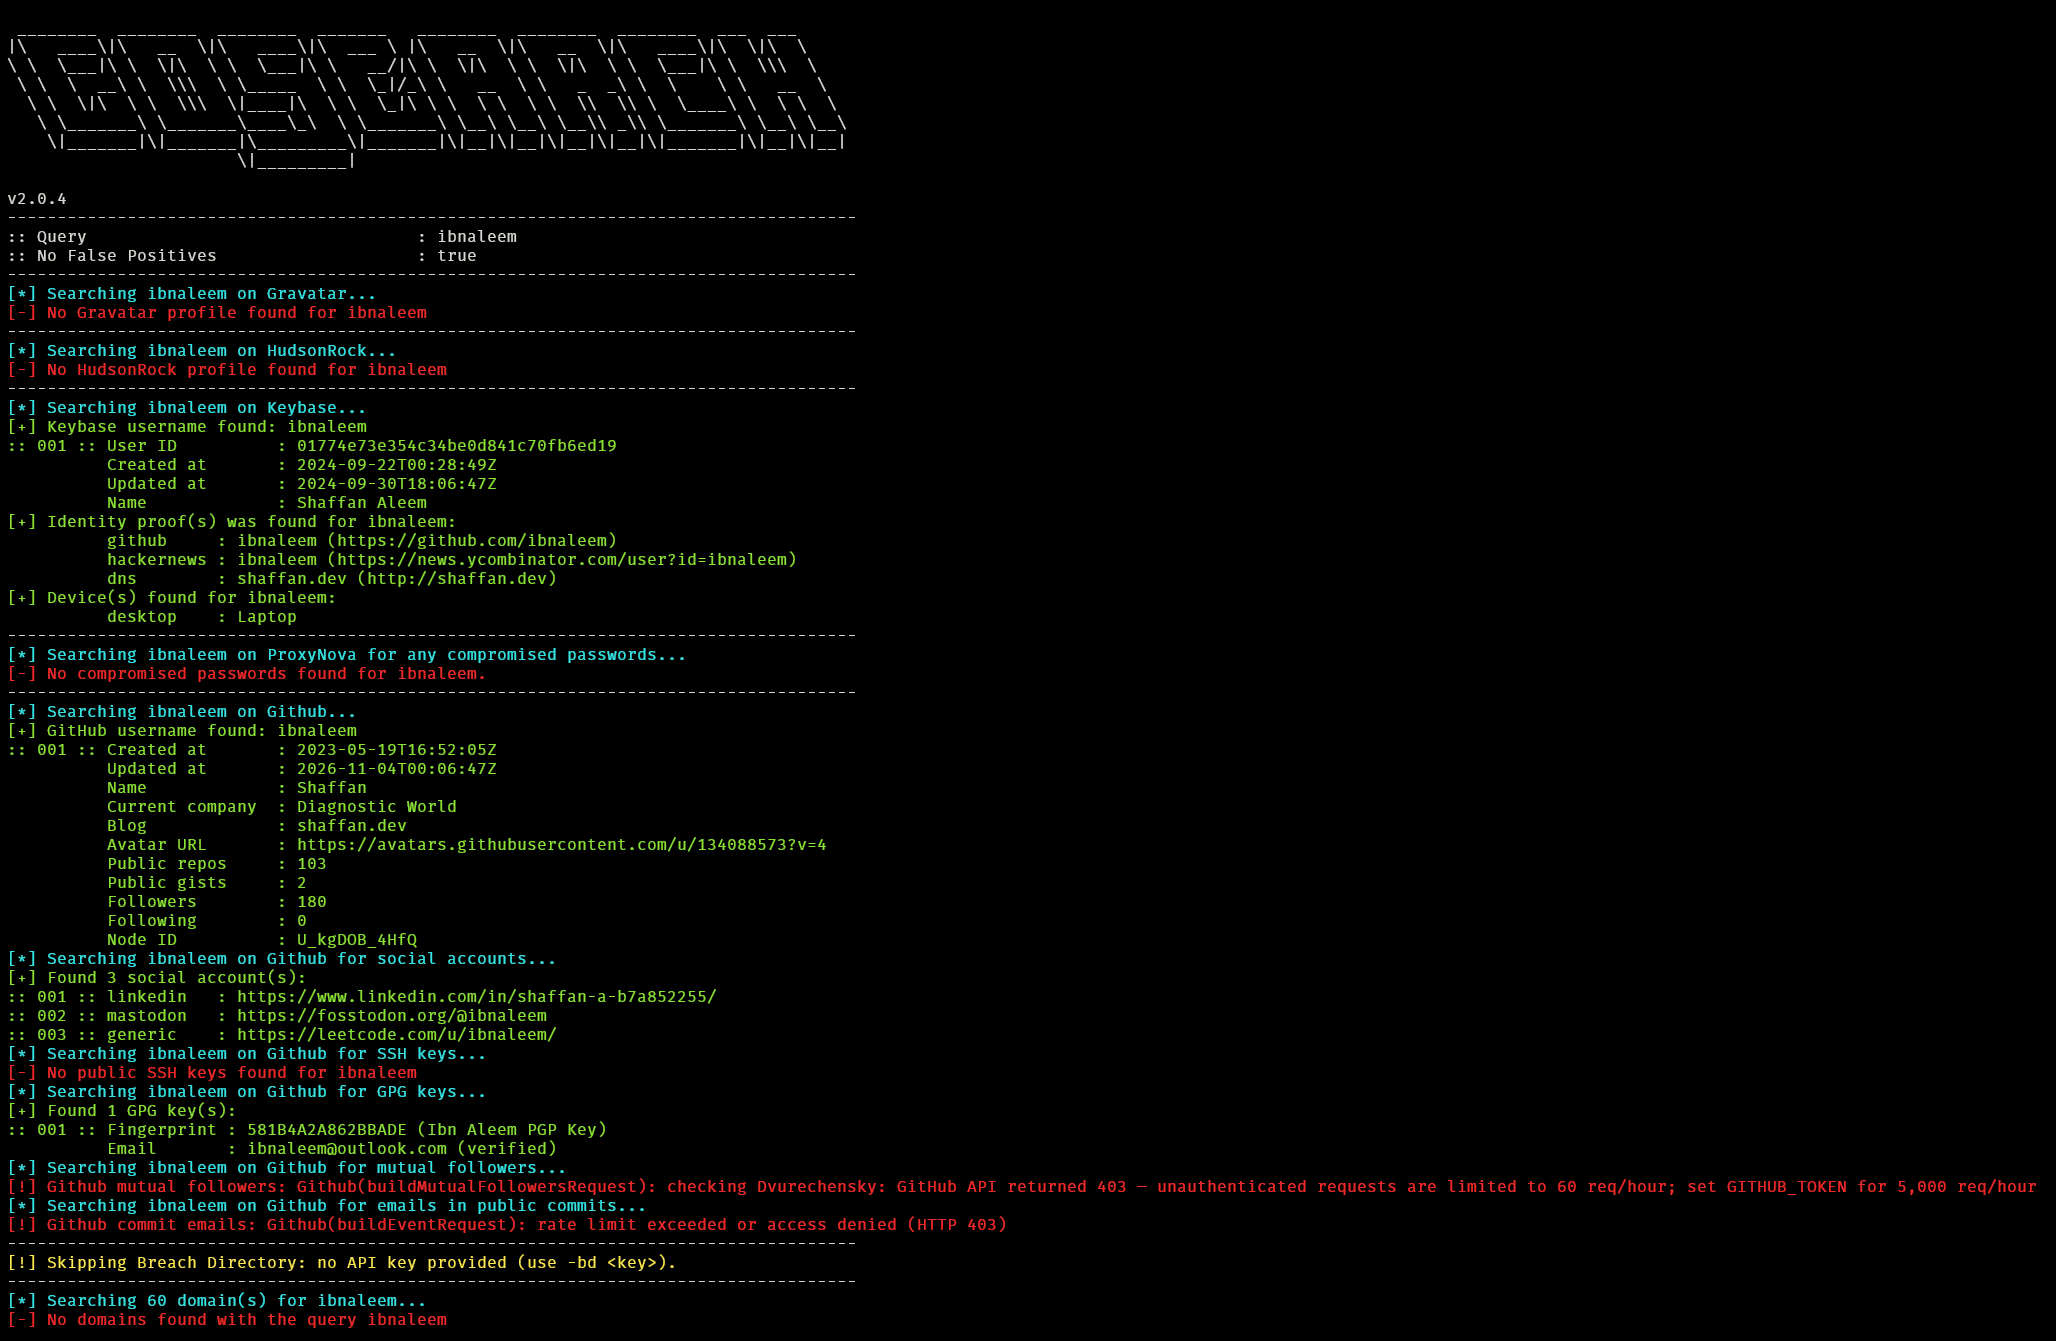


cariddi
Take a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
- 3.8k
- Go
- GPL-3.0
- 6 d ago
Penetration-Testing-Tools
A collection of more than 170+ tools, scripts, cheatsheets and other loots that I've developed over years for Red Teaming/Pentesting/IT Security audits purposes.
- 3k
- PowerShell
- MIT
- 3 y ago



ezXSS
ezXSS is an easy way for penetration testers and bug bounty hunters to test (blind) Cross Site Scripting.
- 2.4k
- PHP
- MIT
- 9 h ago


PowerShell-Obfuscation-Bible
A collection of techniques, examples and a little bit of theory for manually obfuscating PowerShell scripts to achieve AV evasion, compiled for educational purposes. The contents of this repository are the result of personal research, including reading materials online and conducting trial-and-error attempts in labs and pentests.
- 1.2k
- MIT
- 2 y ago


cobalt-arsenal
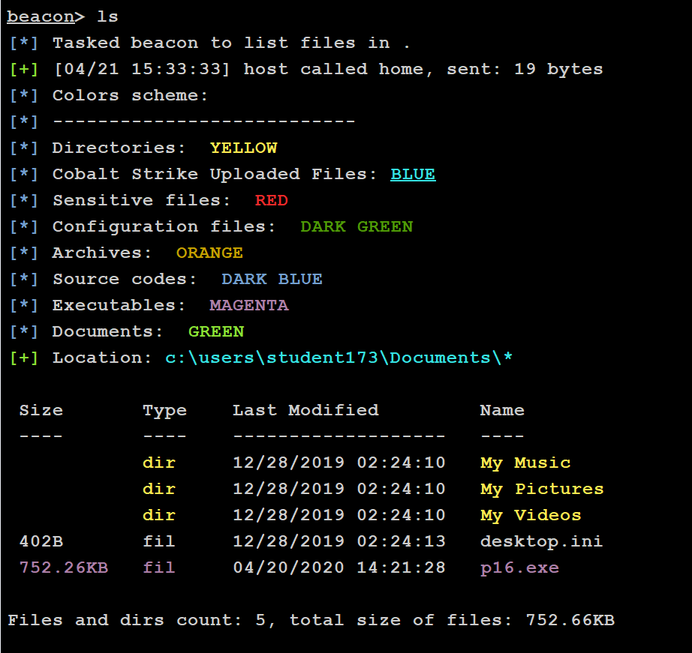
My collection of battle-tested Aggressor Scripts for Cobalt Strike 4.0+
- 1.1k
- PowerShell
- MIT
- 4 y ago


BYOVD
BYOVD research use cases featuring vulnerable driver discovery and reverse engineering methodology. (CVE-2025-52915, CVE-2025-1055, CVE-2026-3609, CVE-2026-8501).
- 1k
- Rust
- GPL-3.0
- 3 mo ago

cain-agent
Real-world AI penetration testing engineer for authorized assessments — built-in cloud module covering AWS/Azure/GCP + Aliyun/Tencent/Huawei clouds. Built on Claude Agent SDK
- 953
- Python
- Apache-2.0
- 5 wk ago

BerylEnigma
ffffffff0x team toolset for penetration testing, cryptography research, CTF and daily use. | ffffffff0x 团队工具集,用来进行渗透测试,密码学研究,CTF和日常使用。
- 697
- Java
- MIT
- 20 mo ago

ThreatHunting-Keywords
Awesome list of keywords and artifacts for Threat Hunting sessions
- 686
- PowerShell
- 16 mo ago
EVTX-to-MITRE-Attack
Set of EVTX samples (>270) mapped to MITRE ATT&CK tactic and techniques to measure your SIEM coverage or developed new use cases.
- 649
- CC0-1.0
- 6 mo ago