RuView
π RuView turns commodity WiFi signals into real-time spatial intelligence, vital sign monitoring, and presence detection — all without a single pixel of video.
- 105k
- Rust
- MIT
- 7 h ago
π RuView turns commodity WiFi signals into real-time spatial intelligence, vital sign monitoring, and presence detection — all without a single pixel of video.
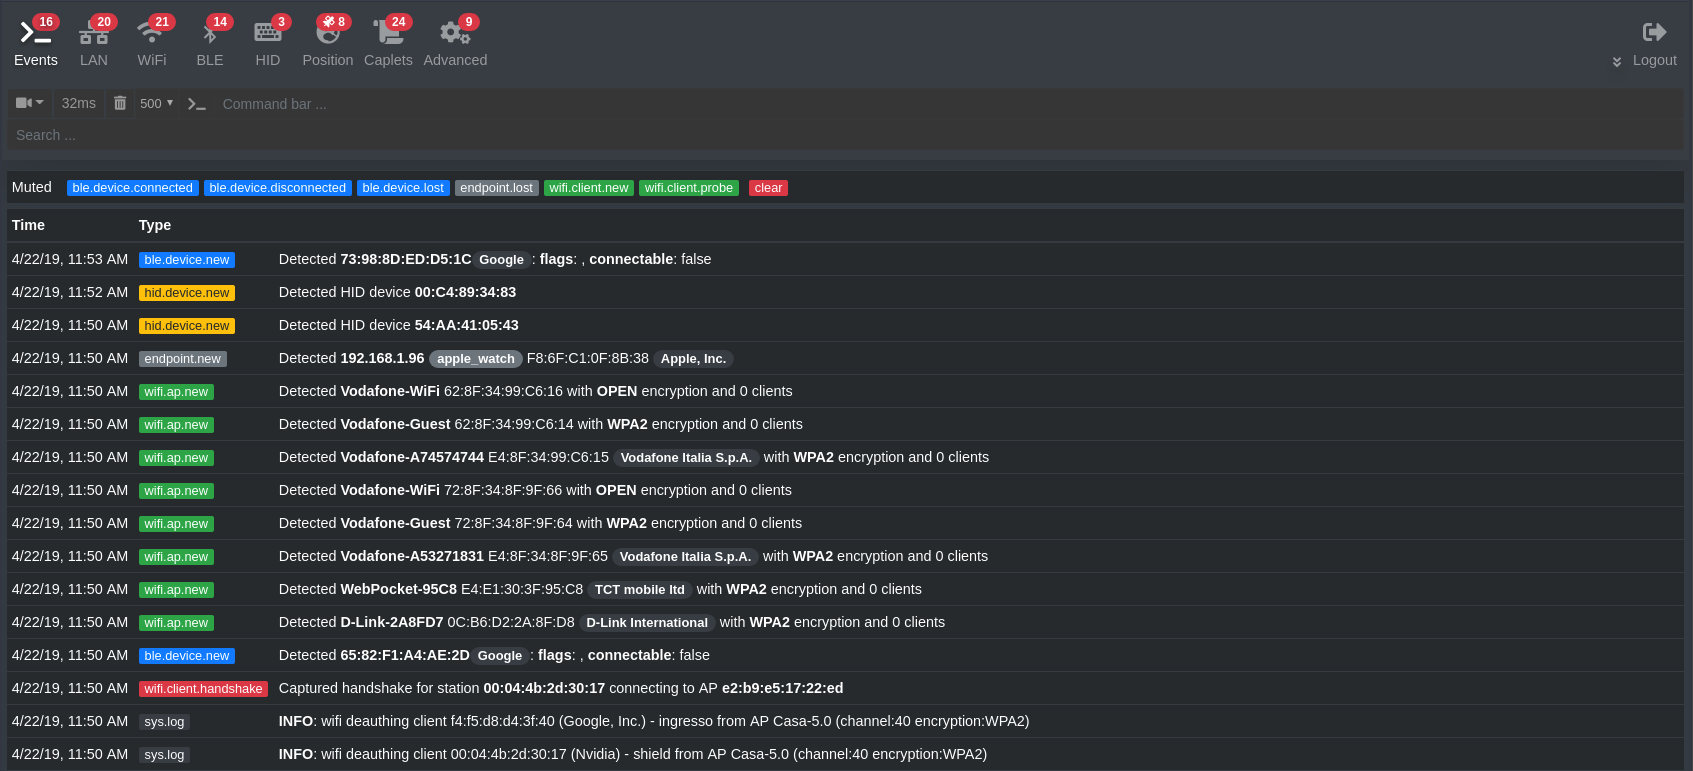
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
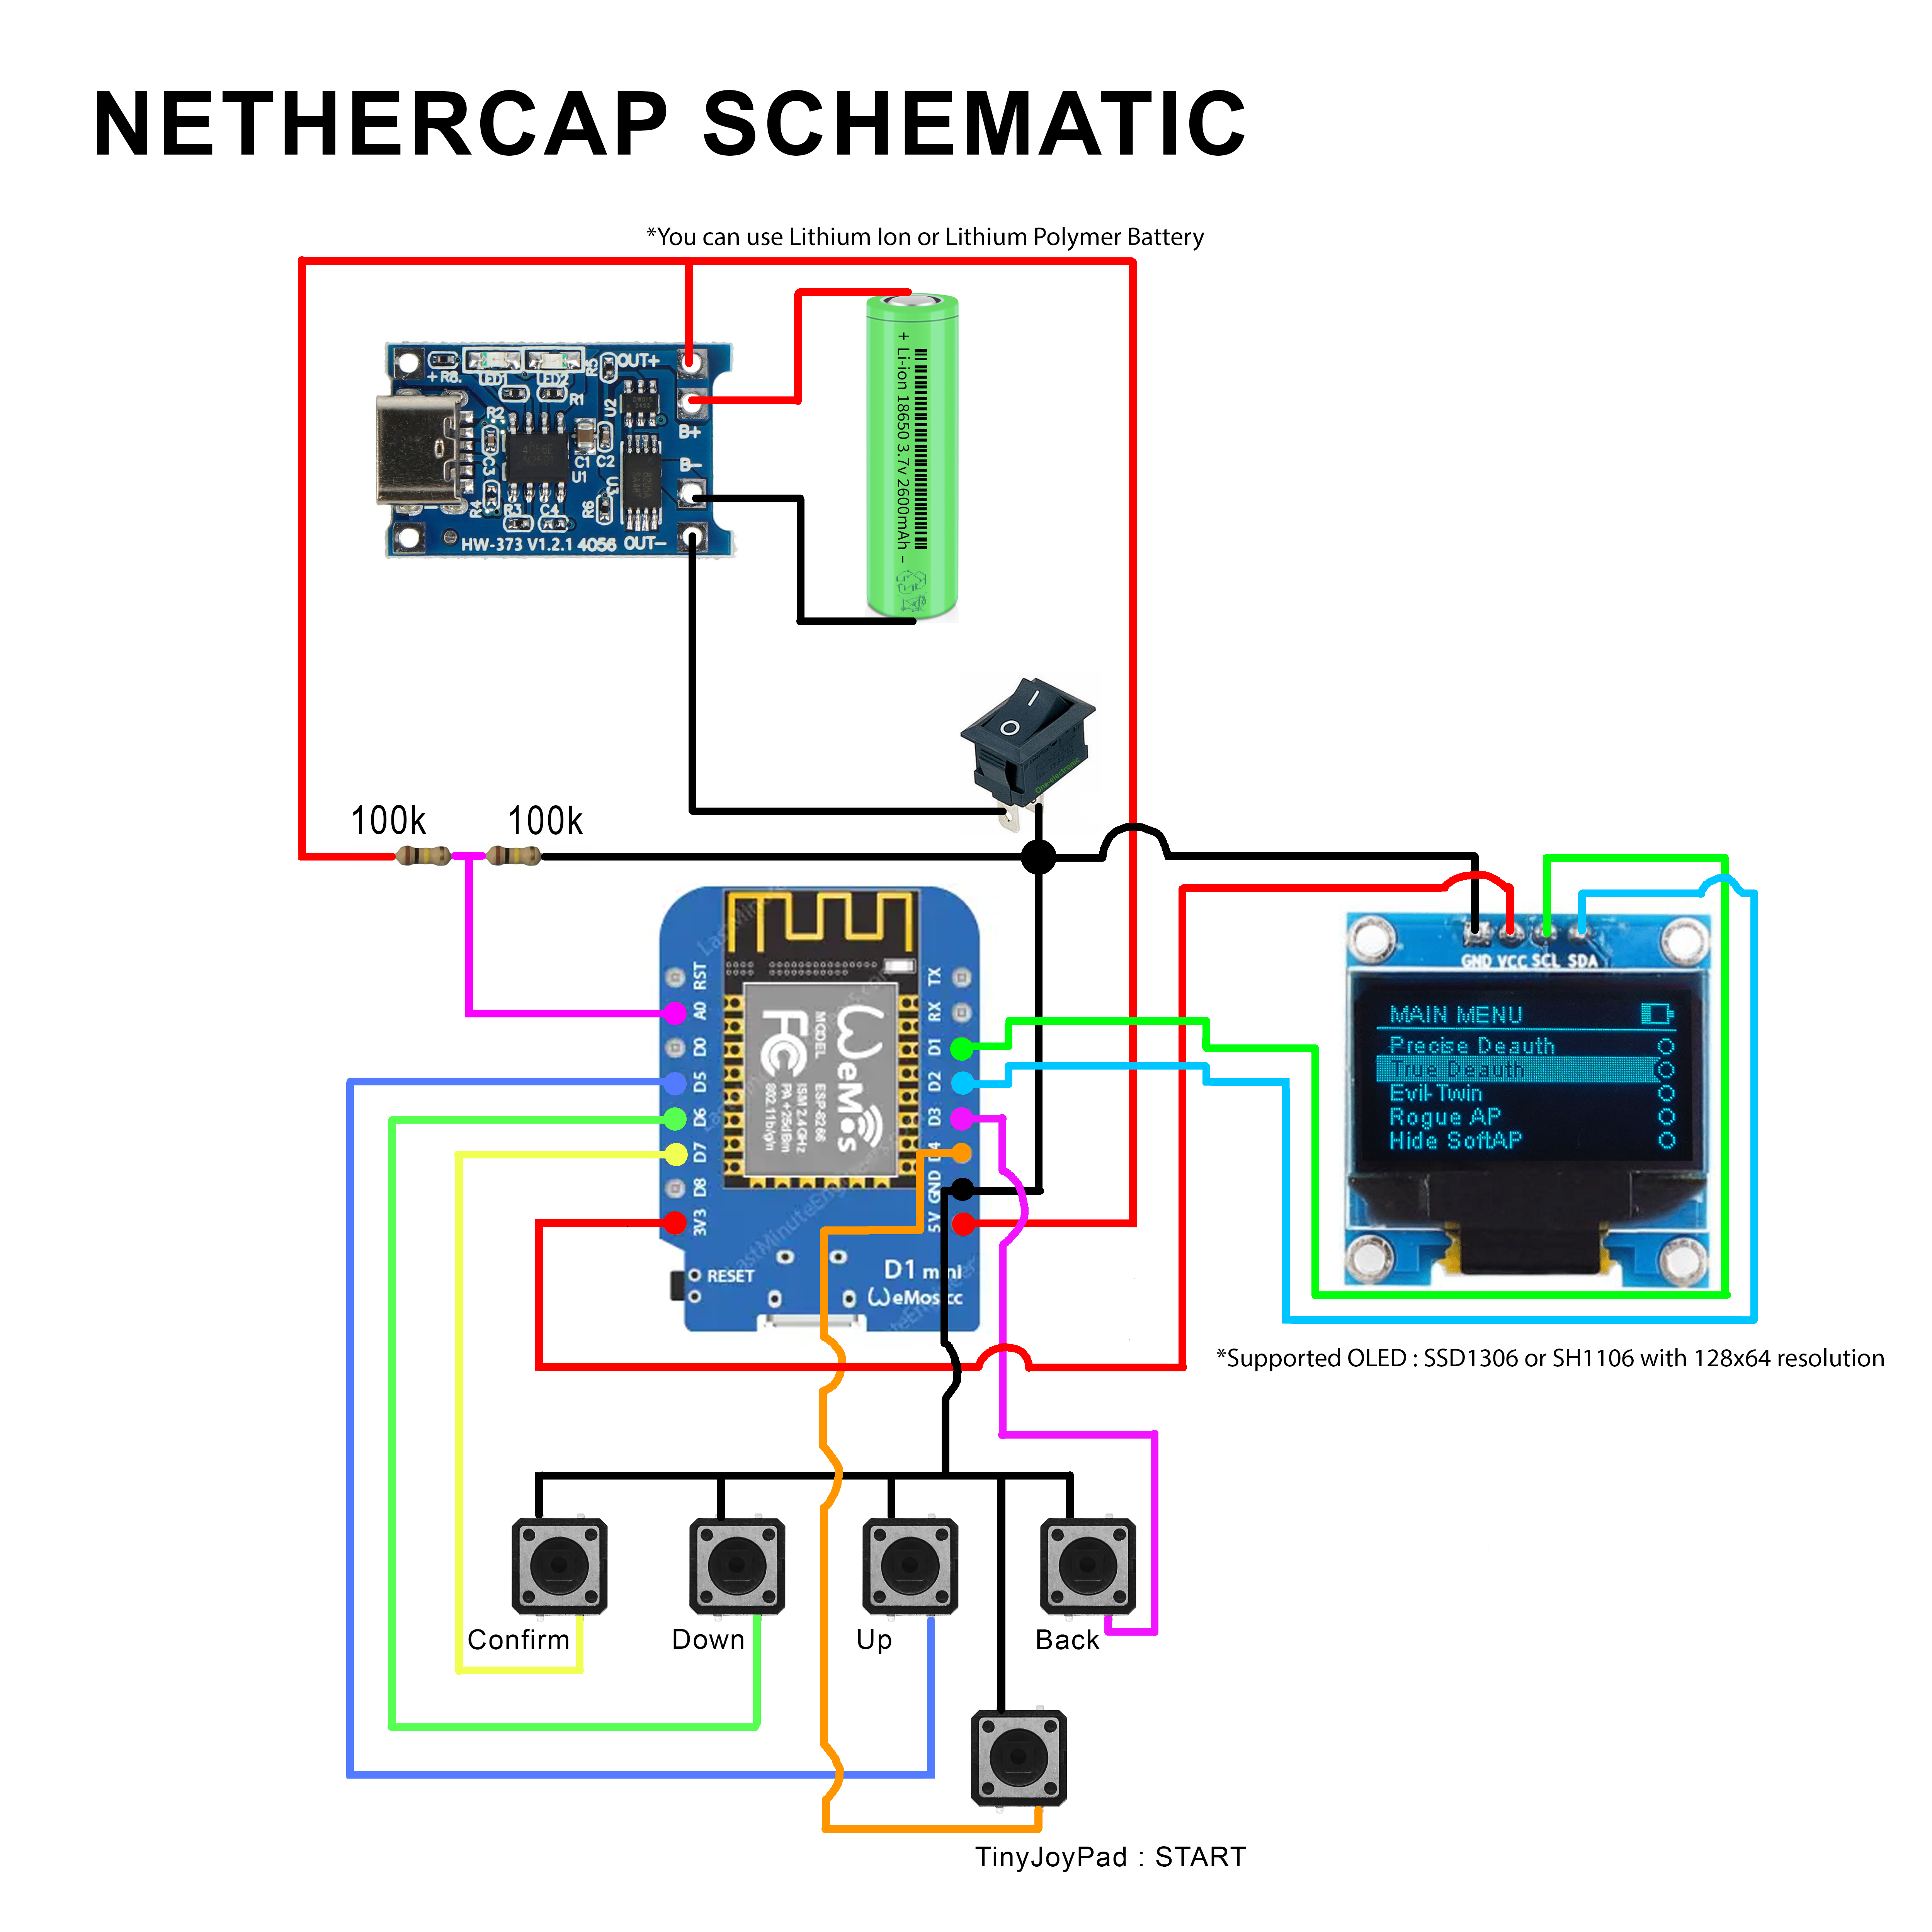
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
A deauth attack that disconnects all devices from the target wifi network (2.4Ghz & 5Ghz), WPA3 also supported (PMF not tested)
One wifi password per device. Ad Blocking & Privacy Blocklists. Policy Based Network Access
Framework designed to automate various wireless networks attacks (the project was presented on Pentester Academy TV's toolbox in 2017).
🍓📡🍍Monitor illegal wireless network activities. (Fake Access Points), (WiFi Threats: KARMA Attacks, WiFi Pineapple, Similar SSID, OPN Network Density etc.)
Turns an Android phone and supported ESP32 board into a portable, no-root wireless security research toolkit.
A reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
Open, hands-on study notes on wireless security & Wi-Fi penetration testing (802.11, WEP/WPA/WPA2/WPA3, aircrack-ng). CC BY 4.0.
Scans all nearby wifi networks and the devices connected to each network for Indoor positioning
POOM is an open-source multitool platform built to Pentest. Play. Create. It is designed for makers, security learners, gamers, and engineers who want a compact device capable of real embedded workflows across wireless security, data capture, automation, and interaction.
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
Raw 802.11 frame injection on ESP-IDF v5+/v6+ via a one-command objcopy --weaken-symbol patch. Enables Authentication (SAE Commit), Deauth, Reassoc, Disassoc, and Control frames (RTS/CTS/ACK) through esp_wifi_80211_tx()
An advanced WiFi scanning and packet sniffing toolkit for the ESP32-C5, featuring a cyberpunk-inspired web interface.
NRSuite a wireless security testing toolkit for Android with no root required. Uses a $3 ESP32 over USB to add Wi-Fi packet capture, WPA2/PMKID handshake grabbing, BLE HID keyboard injection, USB mass storage, and BadUSB payloads to any Android phone through Termux.
Red-team wireless pentesting firmware for the ESP32. Audit WiFi, BLE, IR, Sub-GHz, 2.4 GHz, RFID.
WiFi Dictionary Attack is a compact, Python-based Wi‑Fi security testing script. It scans nearby networks, targets a specified SSID, loads a password wordlist from passwords.txt, attempts WPA/WPA2 connections using pywifi, and reports successes or failures. For authorized, educational security audits only.
Hands-on cybersecurity projects built for learning, experimentation, and practical security research — featuring offensive and defensive tools, automation scripts, and real-world simulations for ethical hacking practice.
razorAP, Bash and Python tool used to generate Fake Access Points for Wi-Fi networks with 802.1X authentication.
WiFi Hacking: Autonomously man in the middle deauthenticate WPA2 wireless networks and packet capture the three way handshake for offline cracking using Kali Linux and a WiFi antenna.
ESP32 firmware for the NRSuite security research toolkit. Wi-Fi/BLE attack and capture modules (deauth, beacon spam, captive portal, BLE HID, BadUSB) over USB serial.
This is a cybersecurity tool created for cracking, testing and securing wifi networks. This tool was built using python.
🍍 Advanced WiFi capture automation for WiFi Pineapple MK7 | Powerful hcxdumptool launcher with MAC filtering, GPS support, multi-channel targeting & OpenWRT optimization | Authorized security testing only
Full-spectrum wireless security MCP server — WiFi, Bluetooth, RF/SDR, NFC/RFID, Cellular/5G, IoT, MouseJack, air-gap, UWB, WIDS/WIPS, compliance. 34 tools, 9 knowledge bases.
Got it! It's an ESP8266 fake WiFi captive portal with DNS spoofing that captures credentials. Here are the best descriptions 👇 Clean & Technical ESP8266 WiFi captive portal with DNS spoofing — creates a fake login page to capture credentials over a rogue access point. Educational use only.
Interactive installer that turns a GL.iNet AR300M into a self-reporting WiFi Pineapple Cloner appliance: flash, brand your AP + captive portal, curated modules, email reports, protected-SSID whitelisting, and hardware-switch recon/deauth+capture. Authorized security testing only.
WifEYE is a high-fidelity sensing suite that transforms commodity smartphone hardware into a tactical RF radar system.