SafeLine
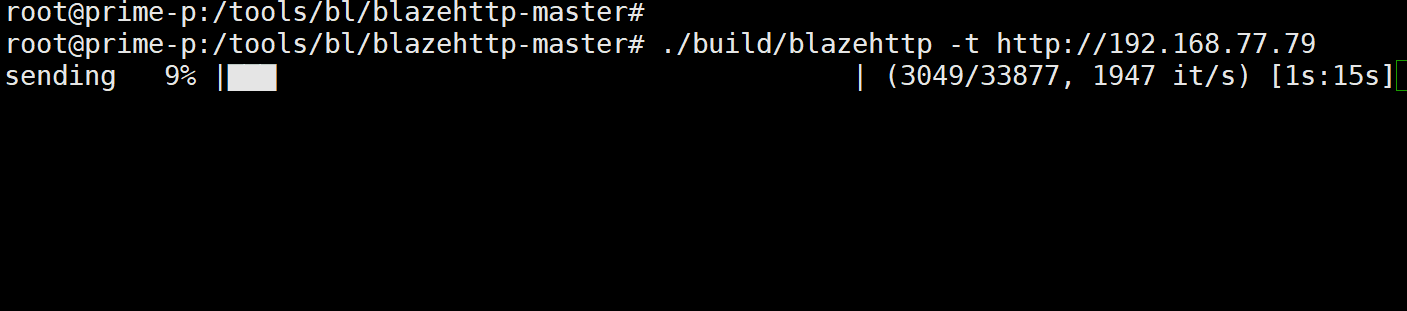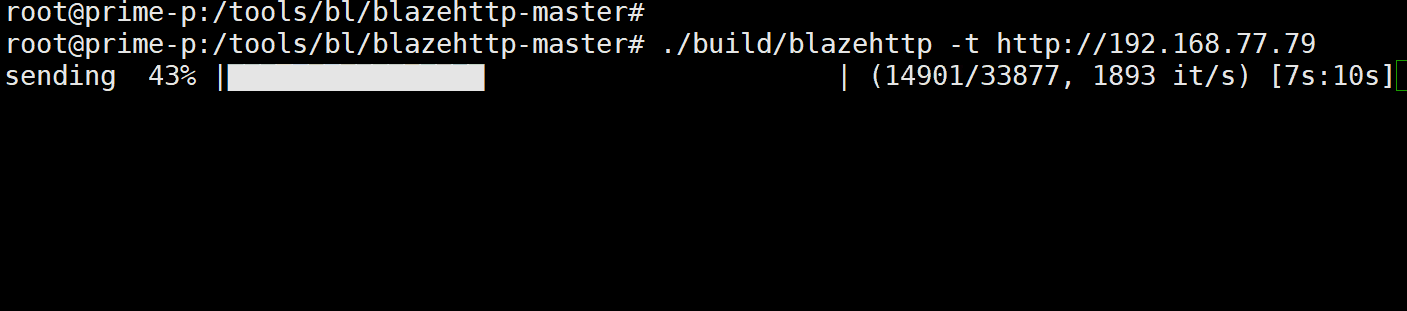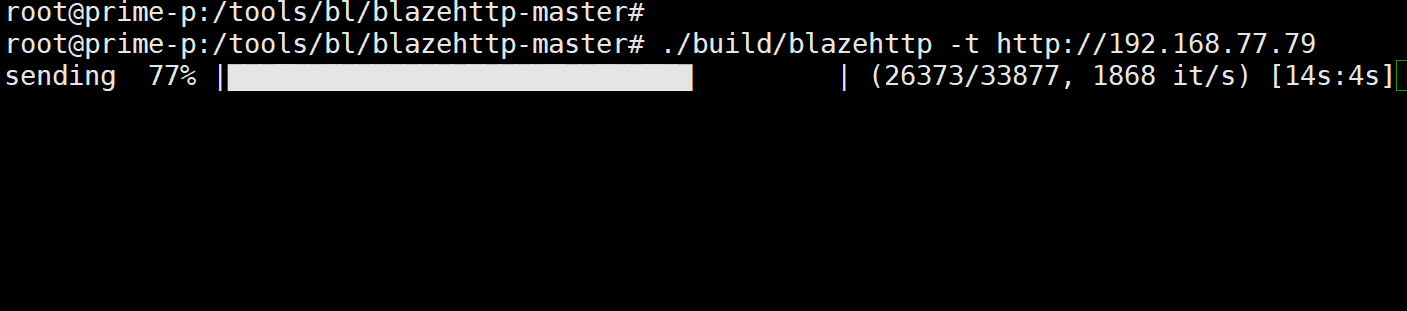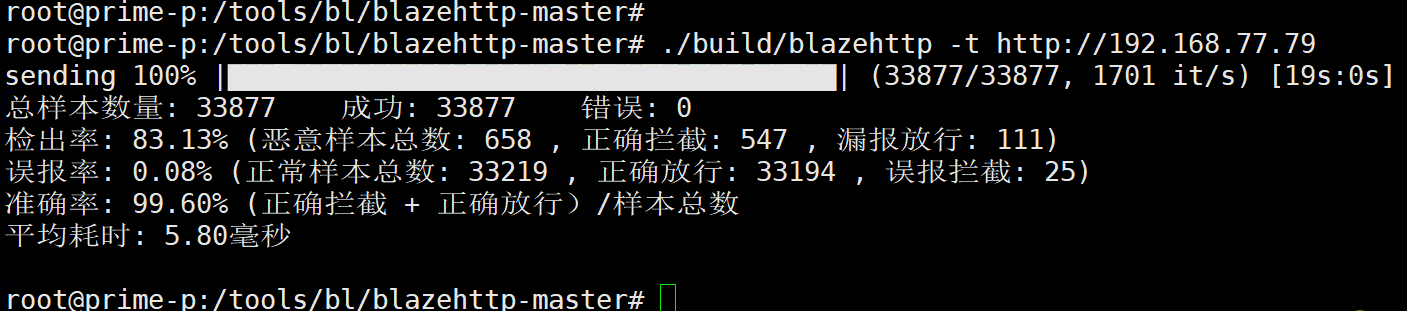
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
- 23k
- Go
- GPL-3.0
- 8 d ago
SafeLine is a self-hosted WAF(Web Application Firewall) / reverse proxy to protect your web apps from attacks and exploits.
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of configurability and hooks. Demo:
Source code for Hacker101.com - a free online web and mobile security class.
A list of resources for those interested in getting started in bug bounties
ezXSS is an easy way for penetration testers and bug bounty hunters to test (blind) Cross Site Scripting.
Industry-leading free, high-performance, AI and semantic technology Web Application Firewall and API Security Gateway (WAAP) - UUSEC WAF.
⚡ Production-Ready AI-Powered Web Application Penetration Testing & Vulnerability Assessment Framework
☕ Latte: the safest & truly intuitive templates for PHP. Engine for those who want the most secure PHP sites.
🛡 Automatically configure your app to follow OWASP security patterns and principles by using HTTP Headers and Middleware
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
Contextual output encoding for Java 8+: HTML, JavaScript, CSS, XML and URI components. Zero-dependency core with optional JSP and Jakarta adapters.
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and automated reconnaissance. Supports REST/GraphQL/SOAP APIs with Nuclei, Turbo Intruder, and external tool integration. OWASP API Top 10 coverage.
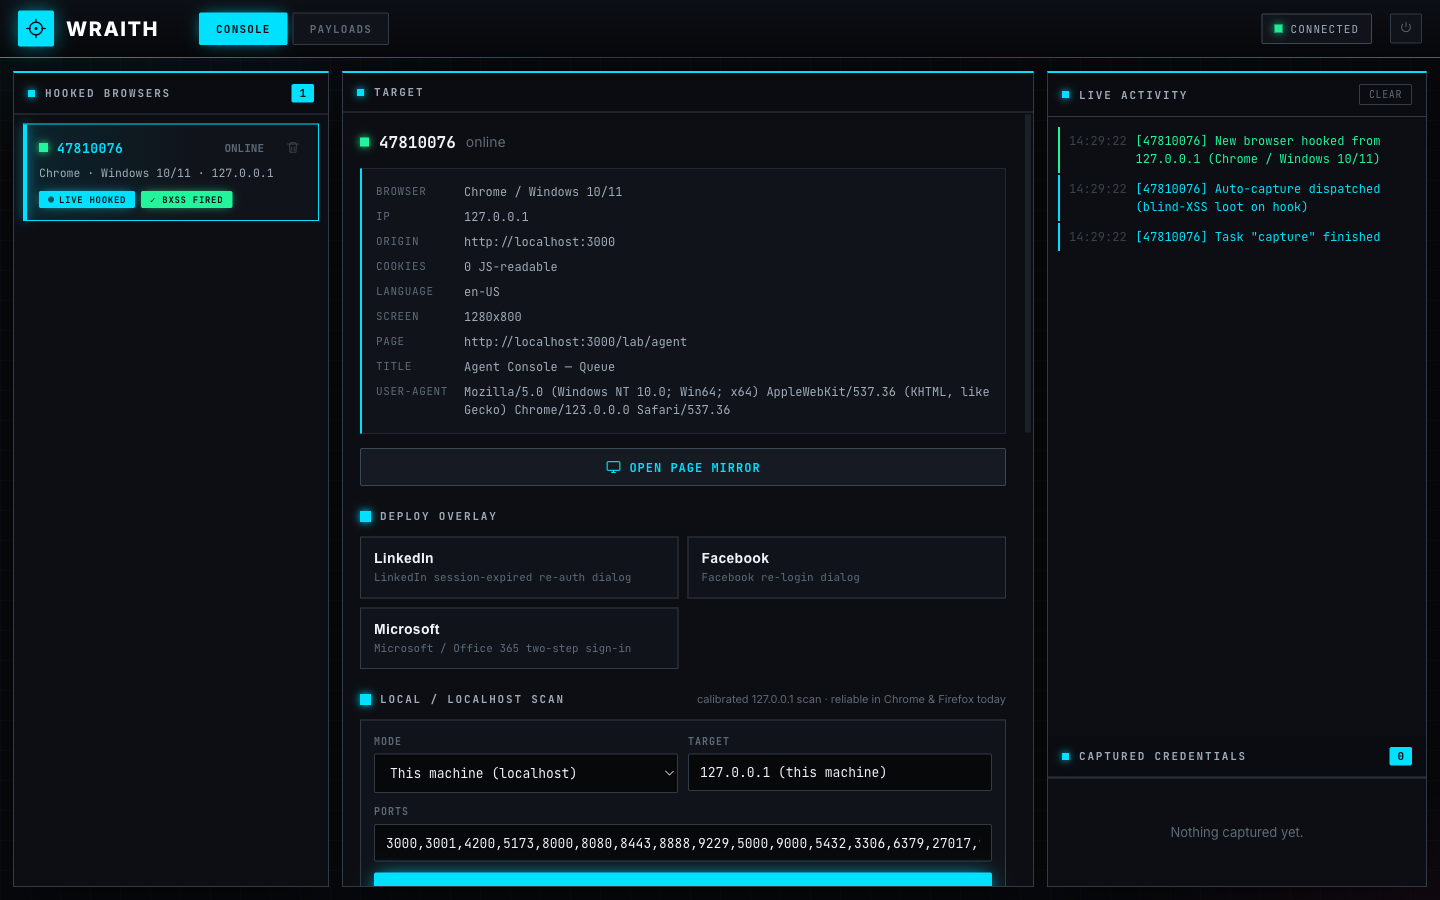
WRAITH — a modern browser-hooking framework (BeEF + blind-XSS successor) for red teams, researchers, and educators. For authorized security testing, research & education only.
Hooks in to interesting functions and helps reverse the web app faster.
Himitsu is a Online/Offline Red Team Tool focused on Password Cracking and Web Vulnerabilities
Security training for the apps you actually ship. Open your browser and start hacking.
Distributed, centrally-controlled Web Application Firewall built on pingap & Cloudflare Pingora. Semantic attack detection, Cloudflare-style rules, CC & Bot defense, automatic TLS, embedded i18n dashboard.
OWASP Hunting: Curated Payloads for Ethical Security Testing and Bug Bounty
PoliteWebScanner is a learning-grade web vulnerability scanner plus AI-assisted report viewer. It crawls safely (queue-based, robots-aware, rate-limited), detects common issues (security headers, cookie flags, reflected XSS heuristics, SQL error patterns), and exports human-friendly JSON/HTML reports with optional AI help for triage and remediation
It's a nginx http module to sanitize HTML5 with whitelisted elements, whitelisted attributes and whitelisted CSS property
A threat actor may inject malicious content into webapp. The payload is reflected in the HTTP request and response, then executed in the victim's browser
An exploit and demonstration on how to exploit a Stored XSS vulnerability in https://anonstress.com.
A threat actor may inject malicious content into webapp. The payload is not reflected in the HTTP request and response, then executed in the victim's browser
URDev’s Ultimate Injection Template is my personal payload collection: a comprehensive reference collection of web injection vectors, focused primarily on client-side execution surfaces in modern and legacy web applications.