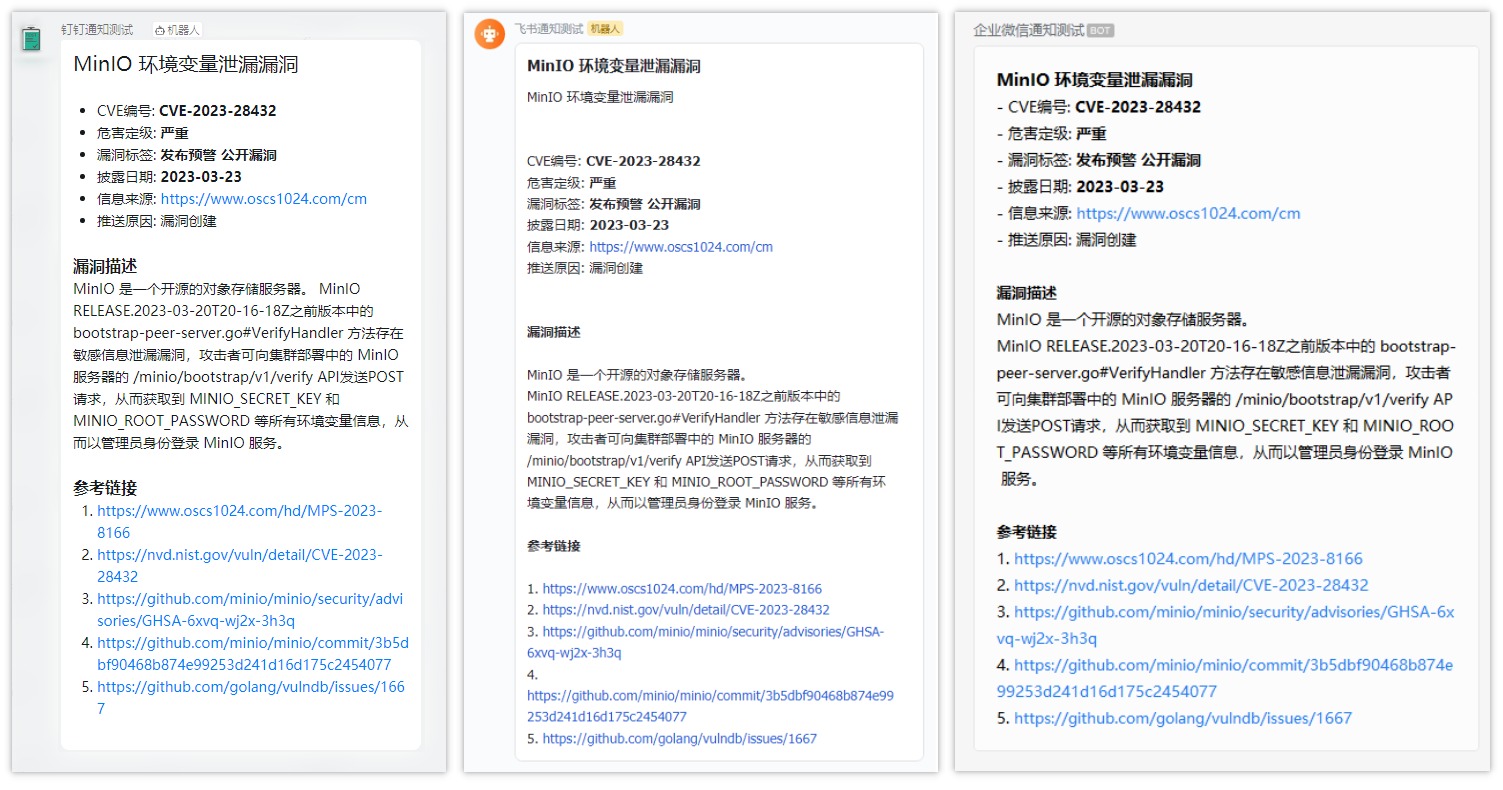
watchvuln
一个高价值漏洞采集与推送服务 | Collect valueable vulnerabilities and push them to various services
- 1.9k
- Go
- MIT
- 3 mo ago
一个高价值漏洞采集与推送服务 | Collect valueable vulnerabilities and push them to various services
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports based on Nmap scan data, and DNS scan information. It can also perform subdomain enumeration to a great extent
Fuzz Introspector -- introspect, extend and optimise fuzzers
Security research and exploit development: vulnerability analysis, exploit chain implementation, post-exploitation tradecraft, and defensive assessment tooling. Covers browser engines, persistence mechanisms, credential harvesting, C2 patterns, and AI-accelerated attack automation.
Why Claude Code leaked: a deep dive into npm packaging failures, source map exposure, and modern supply chain security risks.
Advanced vulnerability management and analysis through data science techniques
AI-guided Go security platform: SAST-directed fuzz-harness targeting, DAST-confirmed reachability, gomu-based mutation testing and one shared findings registry — turning raw scanner alerts into reproduced, verified bugs. So far: 9 vulns + 53 defects found across 34 open-source Go libs.
The task was to reverse engineer an open-source software and a custom binary using various diagnostic tools and security assessment techniques.
Threat modeling of an open-source VPN Client - OpenConnect using Microsoft Threat Modeling Tool
The repository links to the collection of repositories that performs various Software Vulnerability Analysis and Exploits using different tools and methods.
⚖️ The audit AI coding agents can't skip — deterministic facts (deleted-code provenance, symbol invocations, dependency pins) and six-gate claim adjudication for code security audits. Not another scanner.
Python monitor for CVE-2026-109618/109619. It covers patching, temporary risk reduction, suspicious PHP-worker child processes, recent PHP-file detection, email alerts, and cron/systemd deployment.
SecuriFine is a safety-preserving fine-tuning toolkit for cybersecurity that provides a standardized framework to measure, validate, and protect model alignment through automated safety benchmarking, dataset scanning, and differential regression analysis.


