PayloadsAllTheThings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
- 83k
- Python
- MIT
- 3 wk ago
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
API, CLI, and Web App for analyzing and finding a person's profile in 1000 social media \ websites
A list of resources for those interested in getting started in bug bounties
Program for determining types of files for Windows, Linux and MacOS.
Penetration tests guide based on OWASP including test cases, resources and examples.
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements, analyze recon, research exploits, build detections, audit STIGs, and write reports.
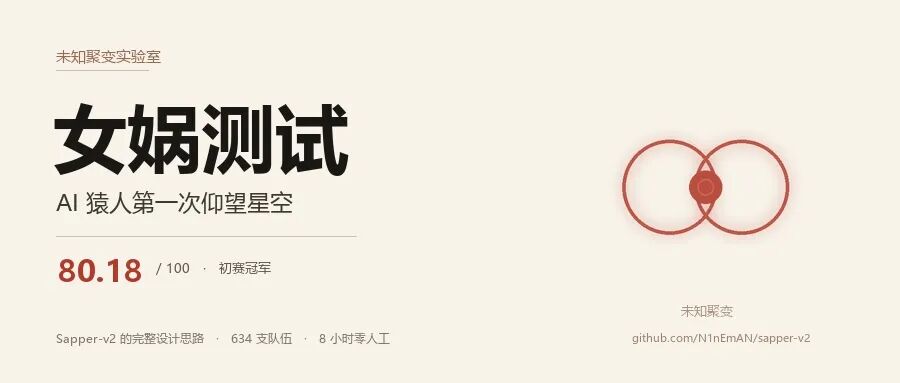
The first fruit of the Nüwa tree — an autonomous AI pentest legion (634-team champion, 8h unattended, 1B tokens beat 4.5B). Not just a tool: evolvable by design. Grow your own fruit on the Nüwa Foundation (Create/Language/History).
ESP32-DIV HaleHound Edition for Cheap Yellow Display - Multi-protocol offensive security toolkit
GraphQLmap is a scripting engine to interact with a graphql endpoint for pentesting purposes. - Do not use for illegal testing ;)
LuaN1aoAgent is a fully autonomous AI-driven penetration testing agent powered by graph-based cognitive reasoning.
A collection of techniques, examples and a little bit of theory for manually obfuscating PowerShell scripts to achieve AV evasion, compiled for educational purposes. The contents of this repository are the result of personal research, including reading materials online and conducting trial-and-error attempts in labs and pentests.
APKHunt is a comprehensive static code analysis tool for Android apps that is based on the OWASP MASVS framework. Although APKHunt is intended primarily for mobile app developers and security testers, it can be used by anyone to identify and address potential security vulnerabilities in their code.
Subdomain and target enumeration tool built for offensive security testing
A deauth attack that disconnects all devices from the target wifi network (2.4Ghz & 5Ghz), WPA3 also supported (PMF not tested)
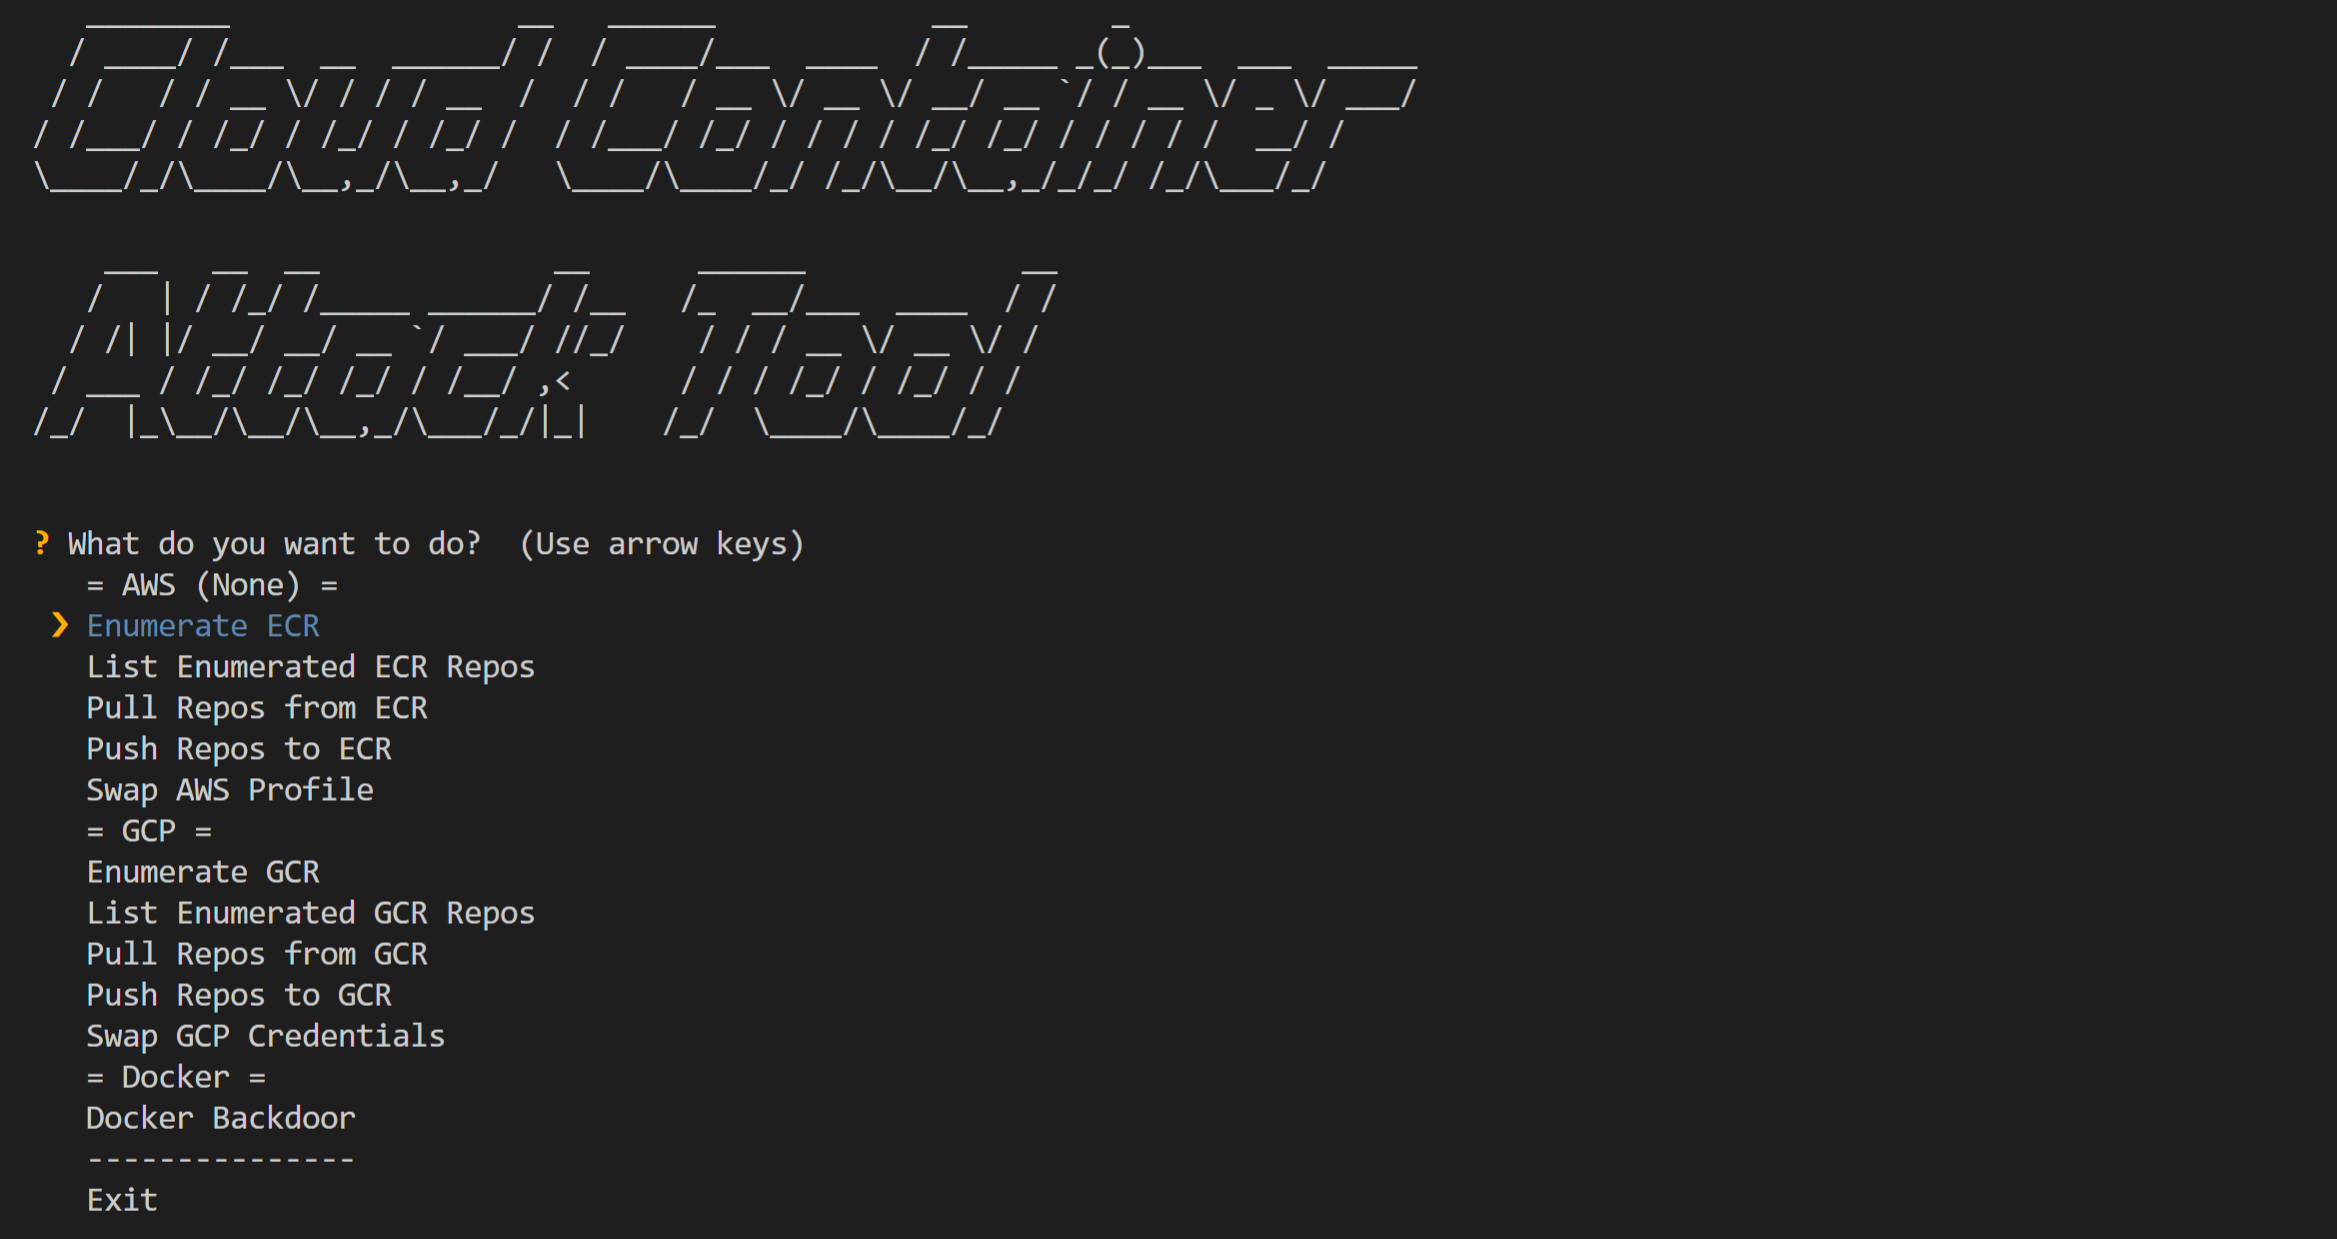
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
Real-world AI penetration testing engineer for authorized assessments — built-in cloud module covering AWS/Azure/GCP + Aliyun/Tencent/Huawei clouds. Built on Claude Agent SDK
A public open sourced tool. Log4J scanner that detects vulnerable Log4J versions (CVE-2021-44228, CVE-2021-45046, etc) on your file-system within any application. It is able to even find Log4J instances that are hidden several layers deep. Works on Linux, Windows, and Mac, and everywhere else Java runs, too! TAG_OS_TOOL, OWNER_KELLY, DC_PUBLIC
AI 自主渗透测试 · 红队作战平台 | 多 Agent 自主推进 · 漏洞情报运营 · 后渗透与 C2 | LLM 三通道轮询 | 全程证据留痕 | 原百度攻防赛冠军项目独立演进版
Selenium powered Python script to automate searching for vulnerable web apps.
Text generation model, used with gguf.
Text generation model, used with mlx.
Text classification model.
Text generation model, used with mlx.
Text generation model, used with gguf.